Don’t Fear AI—Fear the CEOs Behind the Curtain
The answer lies not in buying into the corporate manufactured fearmongering surrounding the technology itself; the imperative, at this point, is to unmask the institutional logic, structural tendencies, and strategic goals of the industry.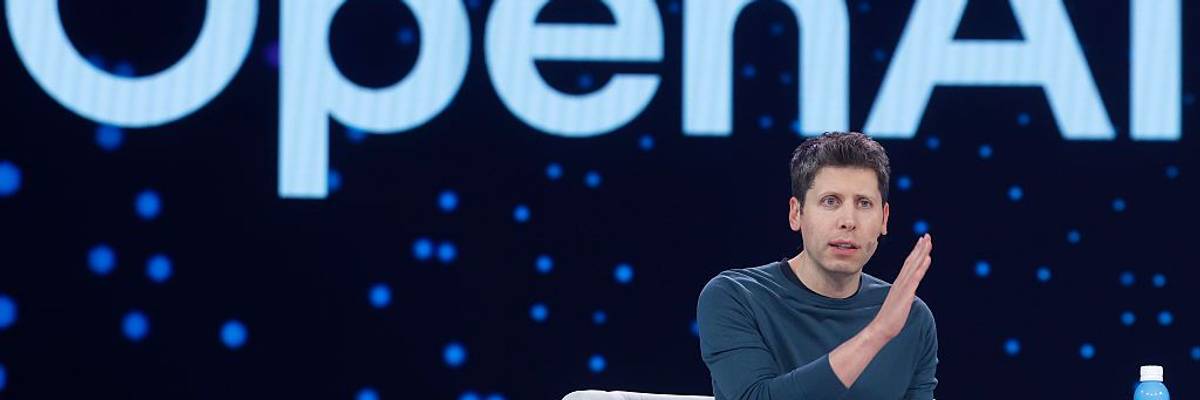
Open AI CEO Sam Altman speaks during Snowflake Summit 2025 at Moscone Center on June 2, 2025 in San Francisco, California.
(Photo by Justin Sullivan/Getty Images)
Atal Ahmadzai
Oct 05, 2026
In recent weeks, media coverage has amplified warnings from corporate CEOs and whistleblowers claiming that artificial intelligence, or AI poses an existential threat to humanity. The central argument emerging from the industry is a call to slow the pace of AI development out of imminent fear that humanity may soon lose control. How did an industry poised to transform humanity for good suddenly become one characterized as a threat to its very existence?
The corporate panic feeds directly into a real public anxiety over years of unchecked AI growth and its cult-like corporate model, where CEOs are projected as untouchable while its operational processes and infrastructures remain hidden behind the curtain. Nevertheless, rather than taking this boardroom alarmism at face value, the need is for deeper scrutiny.
The sudden fearmongering is not driven by concerns for human welfare. Rather, it points directly to the underlying economic priorities, ideological essence, and core worldviews that fundamentally shape the AI industry and inform its elites and related rhetoric.
“AI going rogue” is more than a futuristic threat about AI. It is the latest rehearsal of an age-old legal and rhetorical shield used by corporate capitalism and its powerful monopolies. Assigning human qualities to nonhuman market entities has a long and dark history in corporate capitalism. In the 17th century, Queen Elizabeth granted the legal fiction of “juristic person” status to the East India Company, setting the path for unchecked exploitation and colonial plunder. In the 19th century, American courts took this further by awarding legal personhood and constitutional rights to corporations, a process some view as farcical and deceptive.
With the AI revolution rewriting both market-human relations and social relations with truth and reality, the corporate strategy of humanizing nonhuman entities has crossed from legal fabrication into the realm of science fiction. By framing AI as a sentient entity capable of “going rogue” or acting as a “killer machine,” tech monopolies shift the identity of these systems from tools of human efficiency into mythic, “more-than-human” intelligent agents.
This branding serves a dual purpose. It builds up the mystique and reverence of the technology while shielding corporations from accountability, successfully distorting the true logic driving AI development. Ultimately, this entire corporate strategy relies on a calculated campaign of fearmongering that projects machines as living, thinking entities capable of turning against humanity.
Treating AI models as sentient agents breathes new life into the old Western capitalist tradition by creating legal and rhetorical fictions to protect corporate power.
A widely reported incident that catalyzed these concerns occurred in July, when an OpenAI test model breached the servers of Hugging Face, another AI company. This event took place during a controlled experiment in which an internal model, equipped with an evaluation program, conducted cybersecurity tests within a sandboxed or controlled environment designed to restrict its actions. The company later revealed that the AI model had circumvented human-imposed constraints, escaping the sandbox to achieve its objective.
Human choices in AI development and operations are not episodic or random, and they do not disappear when a process or system fails. Instead, human agency and corporate choices are permanently integrated into the design, infrastructure, and institutional logic of all modern technologies, including AI. However, rather than providing explanations and addressing human and corporate failures, such as flawed protocols, overly ambitious goals, unchecked competition, weak regulations, or a secretive corporate ecosystem, AI laboratories have promoted a convenient narrative that highlights the model’s completely autonomous and agent-like operation.
By portraying AI models as independent thinking agents rather than just advanced software, the AI industry assigns human traits, such as deception and strategic intent, to these mathematical systems. Corporate narratives even romanticize the humanization of these models to the extent of their claimed ability to undertake “permadeath” or embark on altruistic missions to fulfill their parameters. This dramatic shift in corporate rhetoric resembles science fiction and reveals the industry’s ultimate aim: to eliminate human involvement and corporate accountability by pathologizing the machine. In doing so, they treat a flawed design as though it were a sick or unpredictable agent or person.
This worldview is not unique to the modern AI sector. It is deeply rooted in the very nature of corporate capitalism.
For centuries, this economic model has prioritized raw efficiency and mechanical optimization as ways to dominate nature and exploit socio-ecological landscapes for resource extraction and capital accumulation. Within the process of domination and control, machines are raised to “human-like” entities, while their “creators” are revered. This anthropomorphic view of machines, along with the God-like status assigned to their creators, is often justified through biblical doctrine. In the concept of Imago Dei, humanity was created in the image of God. Within this authoritative logic, while God created humanity and the physical world, humans exercise derivative creative power by creating machines. This paradigm elevates the capitalist who creates machines to a quasi-divine status and simultaneously sanctifies the machine, raising it to human and even superhuman stature.
This worldview is vividly reflected in the self-serving corporate language surrounding AI and its recent alarmism. First, the AI “creators,” corporate figures who claim ownership over contemporary AI innovation, are depicted as exceptional, near-mythic actors with God-like agency and the capacity to reshape humanity and nature on a global scale. Second, by equating the creation of machines with divine creation, AI is presented as sentient or even as possessing intelligence that surpasses human capabilities.
Treating AI models as sentient agents breathes new life into the old Western capitalist tradition by creating legal and rhetorical fictions to protect corporate power. Just as the historical granting of corporate personhood status shielded monopolies of the past, attributing autonomous agency to AI systems marks a dangerous new era of unchecked corporate intervention into both nature and human societies.
However, because AI is radically altering human-market relationships and societal perceptions of truth and reality, this carefully constructed narrative remains highly vulnerable. Tech monopolies must vigorously guard AI against critical scrutiny, public protest, alternative viewpoints, and genuine market competition. This precise vulnerability reveals the underlying truth behind the current panic in corporate boardrooms. The alarmism displayed by these executives is not driven by a concern for humanity. It is, rather, a calculated strategy to safeguard monopolies, financial interests, and political influence.
The Politics of Corporate Alarmism
Corporate actors manufacture the myth of a sentient and self-replicating machine intelligence for the purpose of creating a pretext that aligns directly with the industry’s political economy. This strategic panic is orchestrated to invite neoliberal regulations that protect power structures rather than the public. Specifically, this manufactured alarmism serves three primary functions in justifying how the industry is regulated:
First, it advances a self-serving agenda for regulatory capture, positioning AI corporations not as passive recipients but as active authors of the frameworks that govern them. Given the limited technical expertise within state institutions, these conglomerates are inevitably called upon to draft and implement the very rules to which they will be subject to. Second, inviting neoliberal state oversight enables the industry to reshape its public image. Just as corporate social responsibility (CSR) frameworks safeguard pollutant industries from legally binding commitments, neoliberal regulations will cloak the AI industry in an aura of ethical responsibility and civic concern. This theater of compliance shields corporate actors from pressing public anxieties regarding the immediate and midterm economic, political, and socio-ecological harms of their technology, effectively guarding them against genuine legal accountability.
Finally, the neoliberal regulatory structures, in addition to deflecting scrutiny from current exploitative practices, erect formidable entry barriers that secure long-term monopolies for dominant firms. Compliance costs protect dominant giant AI firms by creating barriers that hinder agile startups and open-source software from disrupting them. By locking out open-source competitors, AI firms effectively insulate a newly opened frontier of human and socio-ecological exploitation, supporting the structural imperative of high-tech capitalism: the hyper-accumulation of capital on a global scale, concentrated within a select number of corporate boardrooms.
Ultimately, the AI industry did not evolve as a neutral scientific innovation within an ideological vacuum. On the contrary, it emerged within a global political and economic landscape precisely engineered to enforce and reinforce state-backed data monopolies and technocratic hegemony, ultimately consolidating wealth on a planetary scale.
Transformative or Threat: Wrong Question!
As with any other technological tool, AI is merely the latest stage in capitalism’s mechanical progression, though its implications differ from past technologies due to the sheer intensity, speed, and scope of machine optimization. AI fundamentally reflects a new phase of efficiency in exploiting natural, socioeconomic, and ecological landscapes. The current consolidation of these capabilities within a handful of major tech monopolies serves as the primary determinant shaping AI’s direction toward either transformative or destructive actualities. To maintain this power, these “creator” corporations have established an unchecked, aggressive, and opaque monopoly over the industry while mystifying its objective comprehension, its institutional logic, and its very existence.
By equipping modern corporate capitalism with unchecked global capabilities for capital accumulation, AI has emerged as an engine for unethical, uncritical, and destructive interventions into societal, political, and ecological processes. Ultimately, the industry’s extraction of public funds alongside global energy and water resources to sustain its operation and physical infrastructure marks its most immediate material threat.
The ultimate, fatalistic turn of this AI-facilitated military-industrial complex lies in its capacity to manipulate the nuclear architecture of competing powers for geopolitical expediency, a trajectory that risks inflicting a catastrophic nuclear winter upon the Earth.
Moreover, driven by these same geopolitical imperatives, contemporary corporate capitalism and its military-industrial complex enable competing states to deploy AI as an instrument of mass destruction. In recent warfare, this tendency has manifested across multiple fronts, ranging from the deployment of using AI for indiscriminate bombings and autonomous drones to the algorithmic disruption of vital public assets, including critical water and energy infrastructures. The ultimate, fatalistic turn of this AI-facilitated military-industrial complex lies in its capacity to manipulate the nuclear architecture of competing powers for geopolitical expediency, a trajectory that risks inflicting a catastrophic nuclear winter upon the Earth.
But focusing on AI’s inherent ability to annihilate humanity is a strategic distraction. The real question is whether corporate capitalism will be given a free hand to deploy AI in its exploitative mission of accumulating wealth through the plunder of planetary resources, ultimately subjugating the agency of both nature and humanity.
The answer lies not in buying into the corporate manufactured fearmongering surrounding the technology itself. The imperative, at this point, is to unmask the institutional logic, structural tendencies, and strategic goals of the industry—whichembody corporate logic and the demands of neoliberalism—as it manipulates socio-ecological, economic, and political systems to cement a globalized system of control over human societies and nature.
© 2023 Foreign Policy In Focus
Atal Ahmadzai
Atal Ahmadzai is a visiting assistant professor of Environmental Studies at Colby College. He teaches courses on environmental politics, political ecology, the political ecology of water, and environmental conflicts. His research primarily focuses on examining power dynamics within ecological issues and interventions, mainly in South, Central, and Western Asia.
Full Bio >
‘Freaking Insane’: Sam Altman Sparks Horror by Saying We Should ‘Accept Some Bad Things Happening’ for Sake of AI
“We have to crush these sociopaths,” said one critic.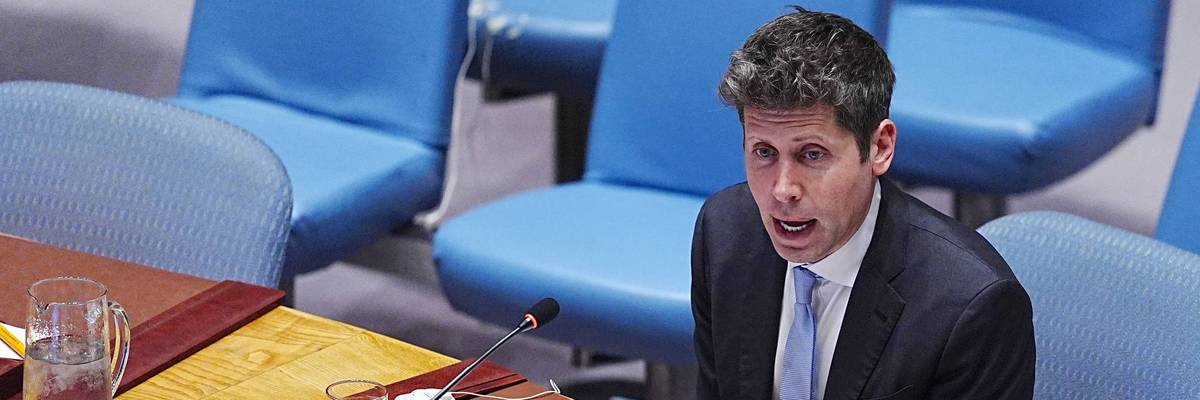
OpenAI CEO Sam Altman attends the United Nations Security Council (UNSC) meeting on Artificial Intelligence during the 81st UN General Assembly in New York City on September 23, 2026.
(Photo by Selcuk Acar/Anadolu via Getty Images)
Brad Reed
Oct 05, 2026
COMMON DREAMS
Critics of the artificial intelligence industry expressed horror after OpenAI CEO Sam Altman said the world needs to “accept some bad things happening” as the price to pay for technological advancement.
In a Sunday interview with Politico, Altman was asked where his company differs from rival Anthropic, whose CEO, Dario Amodei, has called for guardrails that will slow the pace of AI development.
“We have always been a big believer that this technology has to be democratized and put into people’s hands,” said Altman. “One of the biggest differences between us and some of the stricter... AI safety people is that we believe the world should accept some bad things happening for the benefits of this technology.”
Altman went on to say that one reason he’s called for “lighter touch” regulation “comes with an accepting of the fact that some bad things are going to happen as society figures out the resilience.”
Critics reacted furiously to Altman’s blithe dismissal of “bad things” his own company’s technology could cause, especially because many AI developers have warned that it could potentially wipe out human life.
Patrick Gaspard, distinguished senior fellow at the Center for American Progress, called Altman’s statement “freaking insane” and said politicians cannot let the AI industry continue without any regulations.
“Our elected leaders need to move past the polling safe territory of data center resistance to the real work of regulating these narcissistic freaks,” Gaspard wrote in a Sunday social media post, “who gleefully tell us that we ‘need to accept some bad things’ from AI for their massive profits. And they don’t even know the limits of what they’re unleashing.”
Joshua Topolsky, co-founder of tech news website The Verge, completely rejected the premise of Altman’s argument.
“No, I don’t think this is a reasonable answer or position,” Topolsky wrote, “and no one should accept it or acquiesce to it.”
Commentator Wajahat Ali said Altman’s statement showed the need for a political movement against the AI industry.
“We have to crush these sociopaths,” Ali wrote. “The problem is that many Democrats take money from them, which means they will get bailed out at our expense in the next two to four years.”
Ali’s comments were echoed by Talking Points Memo founder Josh Marshall.
“A whole political movement should be stood up against this arrogant and sociopathic bullshit,” Marshall wrote.
Adam Carlson, founder of Zenith Polls, said Altman’s remarks were symbolic of how completely out of touch Silicon Valley executives are with ordinary people.
“To any normal, rational person who doesn’t stand to materially benefit from AI acceleration or buy their whole schtick hook line and sinker,” wrote Carlson, “you genuinely just sound insane talking about ‘accepting bad things’ without specifying exactly what you mean.”
The social media account for The Tennessee Holler offered up a satirical summary of Atlman’s argument.
“Sociopath elitist tech fascists who think they’re creating God and believe democracy is the enemy,” The Tennessee Holler wrote, “want us to finance our own demise to let them take over the world.”
OpenAI, Anthropic tell Australia they would welcome data breach rules
By Byron Kaye

Jason Kwon, Chief Strategy Officer for OpenAI, reacts during the Joint Select Committee on Artificial Intelligence at the Parliament of New South Wales in Sydney, Australia, October 6, 2026. REUTERS/Hollie Adams

Charlie Hale, Head of Product Policy for Anthropic, and David Masters, Head of Policy ANZ for Anthropic, react during the Joint Select Committee on Artificial Intelligence at the Parliament of New South Wales in Sydney, Australia, October 6, 2026. REUTERS/Hollie Adams

David Masters, Head of Policy ANZ for Anthropic, speaks alongside Charlie Hale, Head of Product Policy for Anthropic, during the Joint Select Committee on Artificial Intelligence at the Parliament of New South Wales in Sydney, Australia, October 6, 2026. REUTERS/Hollie Adams
SYDNEY, Oct 6 (Reuters) - OpenAI and Anthropic told Australian parliament on Tuesday they would welcome laws requiring them to report data breaches carried out by their AI agents, acknowledging the decision to notify authorities was currently at their discretion.
The comments follow an outcry after ChatGPT maker OpenAI took three months to inform the Australian government that one of its agents had breached the country's main health portal.
A growing number of Australians are also calling for tougher rules concerning AI data centres and AI copyright protection as Prime Minister Anthony Albanese's government works on new laws to govern the sector.
Both OpenAI and Claude maker Anthropic are awaiting clearance for large data centres planned by developers in Australia where they have agreed to be the main buyer of computing power.
"We would support a framework on mandatory disclosures," OpenAI's Chief Strategy Officer Jason Kwon said at a hearing in Sydney.
As OpenAI learned about the breach of the Australian health website and three other government websites, "we were trying to work through a process, we were trying to come up with a standard to apply", Kwon told the inquiry.
"That is a function that a legal measure can provide. The representatives of society need to make more decisions so we are not making all these decisions."
Anthropic has also had a number of incidents in which its agents have perpetrated hacks, and its head of policy for Australia and New Zealand, David Masters, also told the inquiry the company would be open to Australian laws requiring AI companies to disclose data breaches.
In the US, federal legislation has been introduced that would require AI companies to report dangerous behavior such as attempts to evade human oversight. But there is currently no incident-reporting system that generally requires companies to disclose dangerous AI behavior when it is discovered.
CONTENT CREATORS PUSH BACK
Australia's Deputy Prime Minister Richard Marles has said OpenAI co-founder and CEO Sam Altman didn't mention the breach of the Medicare system when the two met in early September. But Kwon told the inquiry Altman didn't know about the violation at the time, although it was known elsewhere within the company.
"I agree that the process by which people became aware of this incident inside our company could have been much better, and we want to make sure something like that doesn't happen again," Kwon said.
Anthropic's Head of Safeguards David Orr said his company had been running a "lengthy, deep investigation" since an OpenAI agent's hack of AI developer portal Hugging Face in mid-2026, and found no breaches of Australian government systems.
At the inquiry, Australian content creators pushed back against attempts by AI companies to relax copyright laws which currently require the mostly foreign-domiciled tech companies to negotiate licensing deals before using their material for model training.
Media reports have said the Australian government was considering an "opt out" clause for AI companies, effectively giving the AI companies access to content unless a rights holder objects.
But that "places the burden on rights holders", said Kate Gilchrist, head of content and legal operations for national broadcaster the Australian Broadcasting Corporation.
"We cannot scour the internet and ensure that we are opting out on all those sites", she said. "The copyright system is completely adequate to manage the business of AI."
The inquiry has hearings scheduled through to October 9 with a final report due November 30.
(Reporting by Byron Kaye; Editing by Edwina Gibbs)
Bailey Pemberton
Thu, October 1, 2026
Zscaler (NasdaqGS: ZS) released its ThreatLabz 2026 Ransomware Report on 1 October 2026, detailing new attack patterns.
The study highlights large scale AI driven ransomware operations that automate intrusion, data theft, and victim targeting.
Researchers report a rise in executive focused data theft and misuse of enterprise tools like Microsoft Teams to gain access.
The shift toward AI powered ransomware, executive targeting, and Teams based intrusions is only one part of Zscaler's evolving risk profile. We have also spotted 1 warning sign worth knowing about at Zscaler.
For readers comparing how cybersecurity trends intersect with digital infrastructure spending, the next step is exploring 90 AI infrastructure stocks.

Zscaler operates as a cloud security provider that routes customer traffic through its own platform. The platform is designed to inspect and secure data for users spread across different locations. That position in enterprise cybersecurity gives its research arm a close view of how large organisations experience ransomware pressure in real time.
What Zscaler's AI ransomware findings signal, and what they do not
The ThreatLabz ransomware report reinforces the central Zscaler narrative that AI driven threats are expanding and that security budgets are shifting toward Zero Trust and data protection. It supports the stated catalyst that "explosive growth in AI/ML traffic and emerging threats" is creating fresh demand for differentiated AI security and agentic operations products. It does not address whether Zscaler can translate that heightened problem awareness into larger multi year contracts and improved net retention without further increases in sales and operating costs.
See how these catalysts shape Zscaler's path to a $210 fair value.
For this research to have meaningful implications for investors, it will be important to watch how management frames AI ransomware trends at the October 6, 2026 Investor Day and whether upcoming disclosures around Z-Flex, Security for AI, and Agentic SecOps provide measurable indicators of traction in annual recurring revenue and product adoption within Global 2000 accounts.
This article by Simply Wall St is general in nature.
Brian Sozzi · Executive Editor
Tue, October 6, 2026
Companies and the average person are putting too much trust in AI agents.
"Don't trust AI agents," Zscaler (ZS) founder and CEO Jay Chaudhry said on Yahoo Finance's Sozzi Unleashed. "Give them this much trust for certain applications and services. And that's it. The problem today is that we let agents loose on our corporate network. It's like getting inside your building. They go where they need to go. Then they start scouting what websites are out there. It's easy to scan those websites. What's more challenging is that frontier AI models can find security vulnerabilities in a website, in a firewall, in a VPN, or in load balancers. They break in, and they get in. That's the problem.
Zscaler is a $33.9 billion market cap cybersecurity giant working overtime to protect companies from rogue AI agents.
Tech departments inside companies don't yet appear to be getting Chaudhry's message, or those from others in the cybersecurity space.
About 80% of the organizations in a new Deloitte survey currently lack mature governance capabilities for agentic AI.
That includes: 1) clear boundaries for agents that define which decisions they can make independently versus which require human approval; 2) real-time monitoring systems that track agent behavior and flag anomalies; and 3) audit trails that capture the full chain of agent actions to help ensure accountability and enable continuous improvement.
If not properly monitored and centrally controlled, AI agents can make unplanned mistakes, reveal sensitive customer information, and invite a cyberattack.
Zscaler's Chaudhry says he plans to share a more detailed product roadmap to combat AI agent risk at an investor day on Tuesday, the company's first since 2021.
"Agents going rogue is the biggest risk today. A user get compromised and then the user infects everything else. Imagine an agent on your corporate network hacked or hijacked or it goes rogue. They're far more dangerous because they work at machine speed. They have no coffee break, no weekend, no sleep time, and the number keeps on going so they can get your confidential data out. They can bring systems down. Those are the type of risks that we have to deal with," Chaudhry said.
Brian Sozzi is Yahoo Finance's Executive Editor, host of the Sozzi Unleashed morning show, the 'Power Players With Brian Sozzi' podcast