Thursday, October 22, 2026


PHP security flaw: Why websites across Europe went dark and what it means for you
FILE — Alice Lin was the victim of an online scammer, pictured here sitting at her computer at home, Saturday, May 9, 2026, in Alhambra, Calif.
Copyright Copyright 2025 The Associated Press. All rights reserved

By Una Hajdari
Published on

AI models uncovered what OpenAI calls "one of the most impactful" security bugs in recent memory, hidden in PHP for more than a decade. From a Pokémon sleep tracker to the Dutch parliament, websites went dark worldwide to stay ahead of hackers.

Artificial intelligence has exposed two critical security flaws in PHP, a programming language that quietly powers most of the internet, sending organisations worldwide scrambling to shut down websites before hackers can exploit them.

The bugs sat undetected in PHP’s code for more than a decade. It took cutting-edge AI models from OpenAI and Google to turn a long-suspected weakness into a working attack — and now the race is on to close the door.

As AI’s fast-advancing capabilities fuel concern over a new era of cyberattacks, here is what you need to know.

Europe reacts

The Netherlands pulled its DigiD digital identity system, the Overheid.nl government portal and the website of the lower house of parliament, with the Port of Rotterdam, hospitals and the country’s five largest political parties following suit.

Even the Dutch National Cyber Security Centre took its own site down.

Finland’s state IT provider Valtori switched off government web services wholesale “as a precautionary measure,” France’s Interior Ministry put local administration sites into maintenance mode and Germany’s federal IT service ITZBund took down several portals.

CERT-EU, the cybersecurity service for the EU institutions, went further than most, telling any organisation unable to patch immediately to take its websites offline rather than risk being hacked.

The European Commission, ENISA, CERT-EU, Europol and the EU’s network of national cyber response teams also issued a joint statement urging organisations to act immediately, prioritising systems exposed to the internet.

What is PHP and why does it matter?

Created in the early 1990s, PHP is a name that originally stood for Personal Home Page and is the code that runs behind the scenes on roughly seven in 10 websites, according to security firm Wiz Research, which calls it “a backbone of the web”.

While languages such as HTML handle what you see on a page, PHP handles what you do not, such as checking logins, processing payments, serving up content.

It underpins WordPress, Drupal and Joomla, the platforms behind everything from personal blogs to online shops and government portals.

That reach is what turns two bugs into a global event. Wiz said every PHP version released in the past decade is affected by at least one of the flaws, and that even a bare-bones “Hello World” page on an unpatched server could be vulnerable.

A fix was released on Wednesday, with the PHP Foundation telling tech departments around the world that “if you run PHP, it is imperative that you update now.”

Patched versions are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Anything older no longer receives official updates and should be treated as exposed unless a vendor has backported the fix, the European Union’s cybersecurity emergency response team (CERT-EU) warned in an advisory.

The result has been a wave of apps and websites going dark, from the Paris police website to a Pokémon sleep tracker, as developers patch their underlying code. Government sites across Europe were among those pulled offline as a precaution.

How did AI find the flaws?

Both vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619 and rated 9.2 out of 10 for severity, sit in the parts of PHP that nearly every request touches, namely memory management and error handling.

If a web request hits PHP’s memory limit at exactly the wrong moment, the software can be tricked into running an attacker’s code without any login.

The PHP Foundation admits its own developers first spotted signs of the problem in 2024, during an external audit.

A theoretical exploit was sketched out, but with no concrete route to an attack and a tiny core team weighing the trade-offs of a fix, work stalled and restarted for months. The foundation called the delay “a structural failure”.

Then AI got involved. In August, security firm Calif, working on an OpenAI-funded audit of PHP’s source code and using OpenAI’s GPT-5.6 Sol model, reported a fully working remote attack with the same root cause.

OpenAI independently flagged the same issue the same day. Wiz followed with further attack vectors two weeks later, using its own Wiz Atlas tool alongside Google’s Gemini 4 Argon and GPT-5.6 Sol.

“With frontier AI models and the right tools, a single researcher completed in a week what previously would have taken a world-class team months of work,” Wiz researchers wrote.

OpenAI called the discovery “one of the most impactful vulnerabilities in recent memory,” adding that it “marks a new phase, where AI can find security bugs with internet-scale impact”.

The findings were kept under wraps while a fix was developed.

Then, on Tuesday afternoon, the two CVE identifiers leaked onto online forums and social media.

PHP brought its release forward by a day, and Calif mistakenly published — then deleted — a video showing its proof of concept working against several targets, the PHP Foundation said. Copies spread quickly.

“The trouble with tools like AI is that the moment all the information’s out there, people can weaponise it very, very quickly,” Steve Kerrison, senior lecturer in cybersecurity at the Singapore campus of James Cook University, told AFP.

“That’s why everybody’s acting with such urgency to respond to this issue.”

Have sites already been hacked?

Not necessarily. “Taking websites offline does not necessarily mean they have been hacked. It can be a responsible measure to protect systems while security updates are applied,” said Dimitrios Salampasis of Australia’s Swinburne University of Technology.

The PHP Foundation said its security team inspected the proof-of-concept code circulating after the leak and found no functional exploit at the time of release.

“The evidence that security researchers are seeing is that nobody was actively performing attacks using the techniques available,” Kerrison said.

The picture is shifting, however. Web infrastructure firm Cloudflare said on Wednesday it had observed attack traffic aimed at its customers, and CERT-EU warned that the public circulation of technical details raises the likelihood that attackers are already probing the flaws.

Larger institutions, from government agencies to news outlets, should be able to patch relatively quickly. Others may be left exposed for far longer.

“There are sites, systems and people out there who will have no idea about this and still won’t for days, weeks and months,” Kerrison warned.

That could include user-run blogs and small business sites, which hackers could hijack to spread computer viruses, send spam or host malicious content.

Could there be other consequences?

Any data breach could come back to haunt customers long after the patch, if their personal information is harvested for phishing attacks — where someone is tricked into handing over a password or payment details.

The tangled, interlinked nature of online systems also means the risk does not end when you update your own server. Many sites rely on third-party services that may themselves run PHP.

If those third parties are slow to patch, “then even though you patched yourself ... you’re still unsecure,” said Rahat Masood, senior lecturer in cybersecurity at the University of New South Wales in Sydney.

PHP is not the whole story, Kerrison added. Strong cybersecurity means several layers of defence, so that one broken lock does not open every door.

The PHP Foundation, for its part, is using the episode to make a pointed plea. The language runs government services, banks and online stores worldwide, yet its security still rests on a small group of foundation-funded developers and volunteers.

Tools can now find bugs faster than ever, it said, but deciding how to fix them without breaking the web takes experienced engineers.


CYBERCRIME


Websites go dark as AI exposes critical security flaws worldwide


Washington (AFP) – Governments and companies around the world shut down websites as they raced Thursday to protect themselves from hacks after artificial intelligence uncovered critical flaws in a widely used programming language called PHP.


Issued on: 21/10/2026 - RFI

Increasingly powerful AI models can spot weak points in computer scripts that hackers can exploit. © Kirill KUDRYAVTSEV / AFP

PHP helps run about 70 percent of the world's websites – from online stores and news outlets to government services – according to Wiz Research, one of the cybersecurity firms that found the two flaws.

Created in the early 1990s, PHP originally stood for "personal home page" but now means "hypertext preprocessor" and sits underneath popular web design platforms.

"These findings rank among the most severe vulnerabilities discovered in PHP, and arguably in software history," a Wiz blog post said.

Increasingly powerful AI models can spot weak points in back-end computer code that have gone unnoticed by humans for years.

That has heightened cybersecurity fears, with the number of software vulnerabilities discovered worldwide in 2026 on track to roughly double last year's record total.

PHP programmers released a fix Wednesday, and the US National Security Agency told organizations to patch their sites immediately or pull vulnerable systems offline – a call echoed by authorities from Japan to the European Union.

A platform affiliated with China's Ministry of Industry and Information Technology urged the same, warning of "two critical remote code execution vulnerabilities with severe impact" in PHP.

Only sites that run PHP on their own servers are exposed. Many large platforms are built on other programming languages or use operators that could install the fix quickly and were able to stay online.

Rahat Masood, senior lecturer in cybersecurity at the University of New South Wales, Sydney, described the discovery as "quite devastating."

It could allow "attackers to get into your servers without any authorisation, without any username or password," she told AFP.

"Once they are in the servers, they can do anything they want" – from stealing sensitive information to modifying website content – she added, urging institutions to "take it seriously."

'New phase'


Government agency sites in countries from Australia to Finland and the Netherlands were among those that went dark, while services from insurance firms, transport operators and media outlets were under emergency maintenance.

Popular apps, including a Pokemon sleep tracker, were also temporarily taken offline while the fix was implemented, while the foundation that runs Wikipedia warned users they could see outages while it addressed the flaws.

"If you run PHP, it is imperative that you update now," the PHP Foundation, which funds developers working on the language, said in a blog post.
Security firm Calif found the flaws in August using OpenAI’s GPT-5.6 Sol model
 © ANDREJ IVANOV / AFP/File

Volker Dusch, a security engineer at the foundation, told the Wall Street Journal it was the most serious problem PHP had faced in more than a decade, comparing it to Heartbleed, a 2014 flaw that set off a worldwide rush to patch.

Security firm Calif found the flaws in August using OpenAI's GPT-5.6 Sol model, as part of an OpenAI-funded audit of PHP's code.

OpenAI said the discovery "marks a new phase, where AI can find security bugs with internet-scale impact."

Wiz, which is owned by Google, said it found them independently weeks later with help from AI models including Google's Gemini 4 Argon and GPT-5.6 Sol.

The flaws had been reported privately to PHP's developers and kept confidential while a fix was prepared.

AI fuels urgency


Details leaked online Tuesday, a day before the planned release of the fix – prompting the rush to take sites offline before hackers could exploit them.

Steve Kerrison, senior lecturer in cybersecurity at the Singapore campus of James Cook University, told AFP that the fear of hackers using AI to quickly and easily exploit the PHP vulnerabilities had fuelled urgency to react.

So far there has been little evidence of damaging attacks, although data breaches could lead to a wave of so-called "phishing" attacks, where hackers use personal details to steal passwords, down the line.

Larger institutions, from government agencies to news outlets, should be able to fix their websites relatively fast, Kerrison said – but others may be left vulnerable.

"There are sites, systems and people out there who will have no idea about this and still won't for days, weeks and months," Kerrison warned.

That may include user-run blogs that could be weaponised to spread computer viruses, spam people or distribute malicious content, he said.
A Simulated War Must Never Become A Real Military Order – Analysis


The article warns that AI used to design and analyze war games can create a risk that fictional exercise events lose their labels and enter operational decision chains, potentially producing false but consistent reports that commanders treat as real.

Recent examples include a U.S. Army III Armored Corps AI planning experiment with British and Polish partners and NATO’s STEADFAST DUEL 2026, neither of which reported an AI-caused breach, yet the piece stresses that connected tools and lost provenance could allow exercise outputs to affect live systems.

It recommends making exercise-to-operations handoffs an explicit acceptance test through durable provenance, purpose-limited credentials that expire, and deliberate fault-injection trials, aligning with NATO’s revised AI strategy emphasis on traceability and governability.


As NATO and allied forces bring artificial intelligence into military planning, fictional reports and exercise-only permissions must never become operational authority by accident.

On November 9, 1979, American air-defense aircraft left their bases in response to an attack that did not exist. A recorded missile-attack scenario had mistakenly been transmitted beyond North American Aerospace Defense Command headquarters. According to a contemporaneous U.S. diplomatic account, built-in checks exposed the false warning in less than six minutes. The aircraft were recalled; none carried nuclear weapons, and no strategic nuclear unit advanced its alert status.

The simulated attack was fiction. The aircraft taking off were real. The safeguards that stopped the error from spreading were real, too.


That distinction has acquired new urgency as armed forces use artificial intelligence to design, populate and analyze war games. On October 20, the U.S. Army reported that its III Armored Corps had tested emerging AI tools in a multinational planning exercise with British and Polish partners. One day earlier, NATO reported the conclusion of STEADFAST DUEL 2026, a major simulated collective-defense exercise involving all 32 Allies and approximately 8,000 participants. The Army planning experiment and the NATO exercise were separate events; neither announcement reported an AI-caused breach of exercise boundaries.

NATO is also applying AI to exercise design. During a September scripting event, multinational personnel used an AI-enabled environment to develop and coordinate exercise material. In the Indo-Pacific, Australia has opened a Fleet Battle Lab capable of running extended virtual naval war games. These developments promise faster iteration and more demanding training. They also make one old question newly important: when does a fictional report acquire the status of a real military fact?

The most dangerous handoff is not inside the model

An AI system does not need to believe it is fighting a real war to affect one. The consequential issue is what the software treats as evidence, which systems receive its output and what people or tools are permitted to do next. A model may know that it is inside an exercise and still generate a recommendation that becomes dangerous when its simulation origin disappears downstream.

Imagine a fictional missile strike inserted into a multinational command-post exercise. One AI assistant summarizes the episode. A second turns the summary into a staff briefing. A third retrieves that briefing as background and proposes an urgent response. The exercise label is lost along the way. The receiving officer sees three apparently consistent products, although all derive from one invented event. This is a hypothetical failure chain, not an allegation about the exercises announced this month.

Several reports repeating the same story are not three independent confirmations. Before a simulation-derived assertion can enter an operational assessment, someone must establish whether its underlying event occurred outside the exercise. Human approval does not repair a fictional premise that nobody checked.

A more direct path runs through connected tools. The National Institute of Standards and Technology has documented how instructions encountered by AI agents can redirect the use of tools and surrounding applications. The implication for an exercise is conditional but serious: if a training agent has access to operational credentials, live messaging or equipment controls beyond its role, a mistake or manipulated input can leave the rehearsal environment. Writing “exercise only” in a prompt is no substitute for a restriction enforced by the systems that receive the request.

That does not mean war games must be air-gapped from every real system. Live exercises properly use real aircraft, ships, communications and logistics under approved rules. The key is to separate legitimate exercise effects from unauthorized operational consequences. Training tools may support a real unit without acquiring permission to issue that unit a real mission order.

A rehearsal is also visible to the adversary


There is a second boundary, beyond the participating alliance. During NATO’s 1983 Able Archer command-post exercise, Soviet forces took unusual readiness measures. A later U.S. intelligence review concluded that some Soviet leaders may have feared the exercise concealed preparations for an actual attack. The review acknowledged uncertainty about how deeply that concern extended. No AI system caused the episode; its lesson is that an exercise can be misinterpreted by actors who see its external signals but not its internal rules.

An AI-enabled planning system could complicate that problem if it accelerates the production of alerts, assessments and recommendations while obscuring their assumptions. An adversary might interpret an allied precaution as offensive preparation, respond, and have that response fed back into the next assessment. Such a sequence would still depend on real human and military decisions, not an imaginary machine deciding independently to start a war.

Research on AI players in diplomatic and military simulations deserves the same restraint. A peer-reviewed 2024 study observed escalation in simplified multi-agent war games, including occasional simulated nuclear use. In contrast, preliminary 2026 experiments found that AI players sometimes avoided war until the researchers changed a game objective. Neither result estimates the probability of an AI-caused conflict in the real world. Together, they show why the model, the game incentives and the human decision system must be evaluated as one arrangement.

Make exercise boundaries an acceptance test

The practical answer is not to abandon AI-assisted rehearsal. It is to make the passage from exercise to operations an explicit, tested interface. A fictional event should carry durable provenance through summaries, exports, retrieved records and exchanges between national systems. If a generated intelligence product loses its exercise origin, the operational workflow should not silently promote it into verified reporting.

A second requirement concerns credentials and effect. Training agents should use purpose-limited access that cannot authorize operational tasks by default. Where a real interface must participate in an exercise, the permission should name the specific approved effects, the authority responsible and the time at which that permission expires. Moving from rehearsal into operational use should require a separate decision, not a confident recommendation from the AI.

Finally, exercise directors should test whether these boundaries survive mistakes. Deliberately remove an exercise label, insert contradictory reports, replay a stale briefing and route a simulated order toward a protected operational service. Measure what was blocked, what reached a human, whether a downstream task continued after the initiating agent stopped, and how quickly control was recovered. The point is to test the handoff, not merely whether the model can explain what went wrong.


This is a realistic international standard. NATO’s revised AI strategy already emphasizes traceability, reliability, governability and interoperable testing. It does not prescribe the particular exercise-to-operations acceptance test proposed here. NATO and willing partners could add such a test to existing exercise certification and procurement practices without imposing one country’s operational doctrine on another.

The opposing argument is that too many controls will make exercises artificial and slow. The answer is to keep the simulation as challenging as possible while limiting what its outputs may authorize outside it. A convincing fictional enemy and unpredictable scenario are training assets. An untraceable fictional intelligence report in a live decision chain is not.

In 1979, the distinction held because verification defeated a false warning quickly enough to prevent further escalation. AI can make future rehearsals richer, faster and more adaptive. Their success should be measured in part by something less glamorous: whether the system can prove where the rehearsal ends.

A war game should test an alliance’s ability to manage escalation. It must never become the unrecognized cause of it.


About Burak Oktenli
Burak Oktenli holds an MBA and a Master of Professional Studies in Applied Intelligence from Georgetown University. His research addresses the governance of authority in autonomous and AI-enabled systems, and his writing has appeared at the Modern War Institute at West Point, RUSI, RealClearDefense, RealClearMarkets, and Geopolitical Monitor. He is the author of Authority Architectures for Autonomous Systems, a ten-volume series on how authority in autonomous systems is delegated, monitored and recovered, at authority-architecture.me
View all posts by Burak Oktenli →


Catholic Moral Theologians Urge U.S. Federal Court To Support ‘Clear Boundaries’ Around Military AI Usage


By Daniel Payne

Key Takeaways:

A group of Catholic moral theologians, including professors from the University of Dayton, the Pontifical Athenaeum Regina Apostolorum, and Loyola University Chicago, has urged the U.S. Court of Appeals for the D.C. Circuit to support defined normative boundaries on military AI.

The filing supports Anthropic’s request for an en banc rehearing after the court upheld the Department of War’s decision to end its contract and designate the company a national security risk for restricting use of its models in lethal autonomous weapons and mass domestic surveillance.

The theologians argue that autonomous weapons obscure human agency and that mass surveillance violates privacy and human dignity, citing Catholic teachings and Pope Benedict XVI, while noting broader recent cautions on AI from U.S. bishops and Pope Leo XIV.


A group of Catholic moral theologians is urging a federal appeals court to rule in favor of “caution” and “responsibility” regarding military artificial intelligence (AI) usage, with the scholars weighing in on a dispute between the U.S. government and one of the most prominent AI companies.

The scholars — which include University of Dayton professor Jana Bennett, Pontifical Athenaeum Regina Apostolorum bioethics professor Father Michael Baggot, and Loyola University Chicago philosophy professor Joe Vukov — told the U.S. Court of Appeals for the D.C. Circuit that it should support “defined normative boundaries” for the use of AI in warfare.


The dispute stems from the U.S. Department of War’s usage of AI models from Anthropic, a major California-based AI developer. The company had been providing intelligence technology for the government but had forbidden its usage in both lethal autonomous warfare and mass surveillance of U.S. citizens.

The War Department ultimately ended its contract with Anthropic and subsequently labeled the company a national security risk. The D.C. appeals court upheld that decision in a September ruling.

In their filing supporting Anthropic’s request for an “en banc” hearing at the appeals court, the theologians said they were backing the company’s “principled ethical stance on AI use” by the military.

The scholars said they agreed that AI “ought not to be used for mass domestic surveillance,” citing the Catholic Church’s teachings on privacy. They pointed to the Catechism of the Catholic Church’s instruction that “no one is bound to reveal the truth to someone who does not have the right to know it.”

Privacy “is not an absolute right,” they acknowledged, but mass surveillance “clearly oversteps” the principle of privacy and would amount to a “clear violation” of human dignity.

Autonomous weapons, meanwhile, “obscure human agency” and shift responsibility “away from human decision-makers to machines.”


“They accelerate the already rapid military decision-making processes, perhaps to the point of eliminating even the possibility of human involvement,” the scholars said, arguing that “practical judgment and careful decision-making” should “inform all human decisions,” particularly involving life and death.

The theologians quoted Pope Benedict XVI in his encyclical Spe Salvi, in which the late pope acknowledged that developing technology offers “new possibilities for good” as well as “appalling possibilities for evil.”

In the boundaries it set, Anthropic “was acting as a responsible and moral corporate citizen, not as a threat to the safety of the American supply chain,” the scholars argued.

Catholic leadership has been regularly warning of the risks of AI in recent months. The U.S. bishops launched a task force in September to help promote human dignity among the rapid rise of AI technology.

Pope Leo XIV, meanwhile, has been a global voice urging caution on AI, including with his landmark May encyclical Magnifica Humanitas, in which the Holy Father warned that the “pervasive technocratic paradigm” of which AI is a part “threatens to normalize an antihuman vision.”

Earlier this month, meanwhile, the pope cautioned against the spread of AI-produced art, with the pontiff citing the “urgent” need to “distinguish human art from what is produced by machines.”


About EWTN News
EWTN News is the rebranding of the Catholic News Agency (CNA), following the decision by EWTN — which was launched as a Catholic television network in 1981 by Mother Angelica, PCPA — that brings CNA and its affiliated ACI international outlets under a single, unified identity. Previous CNA articles may be foundby clicking here.
View all posts by EWTN News →


Palantir says NATO AI system has no ‘kill switch’ after Starlink disruptions in Ukraine

Source: AP Photo
Copyright Copyright Business Wire 2025.

By Jonathan Benton
Published on


The American software firm says it cannot shut off NATO AI systems amid European fears of dependence on US tech following disruptions to Ukraine’s Starshield access.

US software company Palantir has sought to reassure European allies that its military AI system used by NATO has no “kill switch”.

Palantir’s executive vice president for the UK and Europe, Louis Mosley, told Reuters on Wednesday that neither the company nor the US could switch off the Maven Smart System AI platform used by NATO’s military headquarters and several European armed forces.

“What we have seen in the news over the past few days around Starlink is extremely concerning,” Mosley said in an interview in Brussels.

“But as concerns Palantir, I can provide categorical reassurance that where customers have bought our software, they are in full operational control of that software,” he said.

“There are no kill switches. There’s no ability for Palantir or the US government to reach in and switch it off.”

It follows recent disruptions to Ukraine’s Starlink and Starshield services, which raised alarm over the reliance on US tech firms.

On 13 October, Kyiv accused Washington of deliberately slowing Starshield, the SpaceX-operated military communications system that Ukrainian forces depend on at the front, as well as SpaceX’s civilian satellite network Starlink.

Reports later emerged that the White House had ordered Elon Musk’s SpaceX to limit Ukraine’s access to Starshield, the military-grade version of the Starlink satellite network.

Musk defended himself on X, and claimed that the “Starshield systems are owned and controlled by the US government. Any limits on speed or usage are decided by the US military and ultimately POTUS.”

To which US President Donald Trump replied, saying, “it wasn’t me, and I don’t think it was Elon. I don’t know if it was anybody. From what I understand, it’s the same as it’s always been.”

The lack of clarity over who was responsible for the decision is one concern. But for European leaders, the prospect of the Trump administration using US technology that Europe has become so reliant upon as political leverage against its allies is even more alarming.

Palantir’s Maven system

NATO currently uses Palantir’s Maven system, which relies on AI to process large volumes of battlefield data from satellites, radar, drones and other sensors to speed up decision-making.

Palantir won a €480 million tender with NATO in 2025 to supply Maven to the alliance. It has since been deployed at NATO’s Allied Command Operations at the Supreme Headquarters Allied Powers Europe (SHAPE), and in June this year it achieved “full technical operational capability”.

Some European NATO members, including France and Germany, have opted out of Maven, alarmed at the possibility of a private company having so much control over battlefield operations.

“Allowing industry personnel access to national German datasets is out of the question," German Vice Admiral Thomas Daum said earlier this year.

France has meanwhile developed its own service, Arcadia, in an effort to build its own defence data ecosystem and maintain technological sovereignty.


Barclays to cut 5,000 jobs as it turns to AI to improve efficiency

File - A general view shows the Barclays Investment Bank, Monday, 7 April 2025, in New York.
Copyright AP Photo/Yuki Iwamura

By Doloresz Katanich
Published on

British bank Barclays said on Thursday it would cut around 5,000 jobs, or roughly 5% of its global workforce, by the end of 2026 as it turns to AI and other technology to streamline operations and improve efficiency.

Barclays shares edged lower in London after the bank said on Thursday it would cut around 5,000 jobs, including around 1,000 already cut in the first half of the year.

The announcement came alongside an earnings update that showed Barclays’ net profit grew 13% in the third quarter, helped by surging income in its equities division.

Barclays said in an earnings presentation that it was implementing “organisational simplification and technology change efficiency driven by AI”.

About 60% of the job cuts affect support functions, including developers, as AI makes staff more productive, according to the bank.

Will Howlett, a financial analyst at Quilter Cheviot, said the announcement illustrates "just how significantly AI and automation could reshape the banking industry over the next few years".

"Banks have spent heavily on technology for years, but we are increasingly reaching the point where that investment translates into fewer people being required to run the business," he said, adding that "Barclays expects its efficiency measures to deliver more than £1.1 billion (€1.31bn) of savings, which should help bring down costs and improve profitability."

The bank’s profit attributable to shareholders rose to £1.65 billion (€1.97 billion) in the third quarter from £1.46 billion (€1.74 billion) in the July–September period a year earlier.

Barclays chief executive C. S. Venkatakrishnan said he was pleased with the bank’s operational and financial momentum, and said the investment bank division “delivered strong equities performance”.

Income from equities jumped 47% year-on-year, while total group income for the quarter climbed 3% to £7.37 billion (€8.79 billion).

"The investment bank was weaker, particularly in fixed income trading, but Barclays remains on track against its longer-term targets," said Howlett. He added that "the question is increasingly whether Barclays can turn technological investment and a smaller workforce into sustainably lower costs without compromising growth." If it can, he said, "there is still considerable scope for improved returns.”

The bank also announced a £500 million (€596 million) share buyback.

The AI “announcement comes as the company failed to match expectations with its third-quarter performance — with the unveiling of a healthy share buyback failing to entirely ease investors’ disappointment”, noted AJ Bell investment director Russ Mould.

He added that while costs increased across the wider group, there are two "major clouds over the business".

“The first being a widely expected increase in tax on the sector in next week’s (UK) budget and the other being a reported probe into possible misrepresentation of risks in its private credit portfolio,” Mould said.

According to the FT, the Bank of England was examining claims that Barclays had understated risks linked to financing for private credit funds. The concern is whether Barclays made these exposures look less risky in its books, allowing it to hold less capital to cover potential losses.

Barclays has said its private credit exposure is treated in line with accounting and regulatory capital requirements.

AI use surges in Poland, reaching four in 10 people

AI use surges in Poland, reaching four in 10 people
/ Image by Tomislav Jakupec from PixabayFacebook
By bne IntelliNews October 22, 2026

The share of people in Poland using artificial intelligence (AI) tools jumped to 39.8% in 2026 from 22.7% a year earlier, the statistical office GUS said on October 21.

The 17.1pp increase confirms the rapid spread of AI applications among Polish consumers, although substantial differences persist between generations.

The figures, covering people aged 16-74, refer to those who reported using AI tools during the three months preceding the survey.

AI adoption was highest among the youngest respondents, with 72.5% of those aged 16-24 reporting using the technology, up from 49.3% in 2025.

AI usage reached 62.1% among people aged 25-34, up from 39.5% a year earlier, while the share for those aged 35-44 increased to 47.9% from 29.4%. In the 45-54 age group, uptake more than doubled to 35.9% from 15.3%.

The technology remains far less popular among older generations, although adoption is accelerating. Usage among 55-64-year-olds climbed to 20.8% from 7.5%, while the oldest group surveyed, those aged 65-74, recorded an increase to 9% from 2.6%.

AI adoption is also accelerating in Poland's corporate sector, with 17.8% of businesses reporting using the technology, more than double the 8.7% recorded in 2025.

The share of companies using AI to generate images, audio or video climbed to 9.9% from 2.9%, while those employing text- or voice-generating technologies increased to 9.7% from 5.3%.

Marketing and sales were the most common applications, accounting for 11.1% of businesses, followed by office work and management decision-making processes, at 9.6%.

Refusing to cross, unable to escape: Seafarers recount Hormuz dangers to Euronews

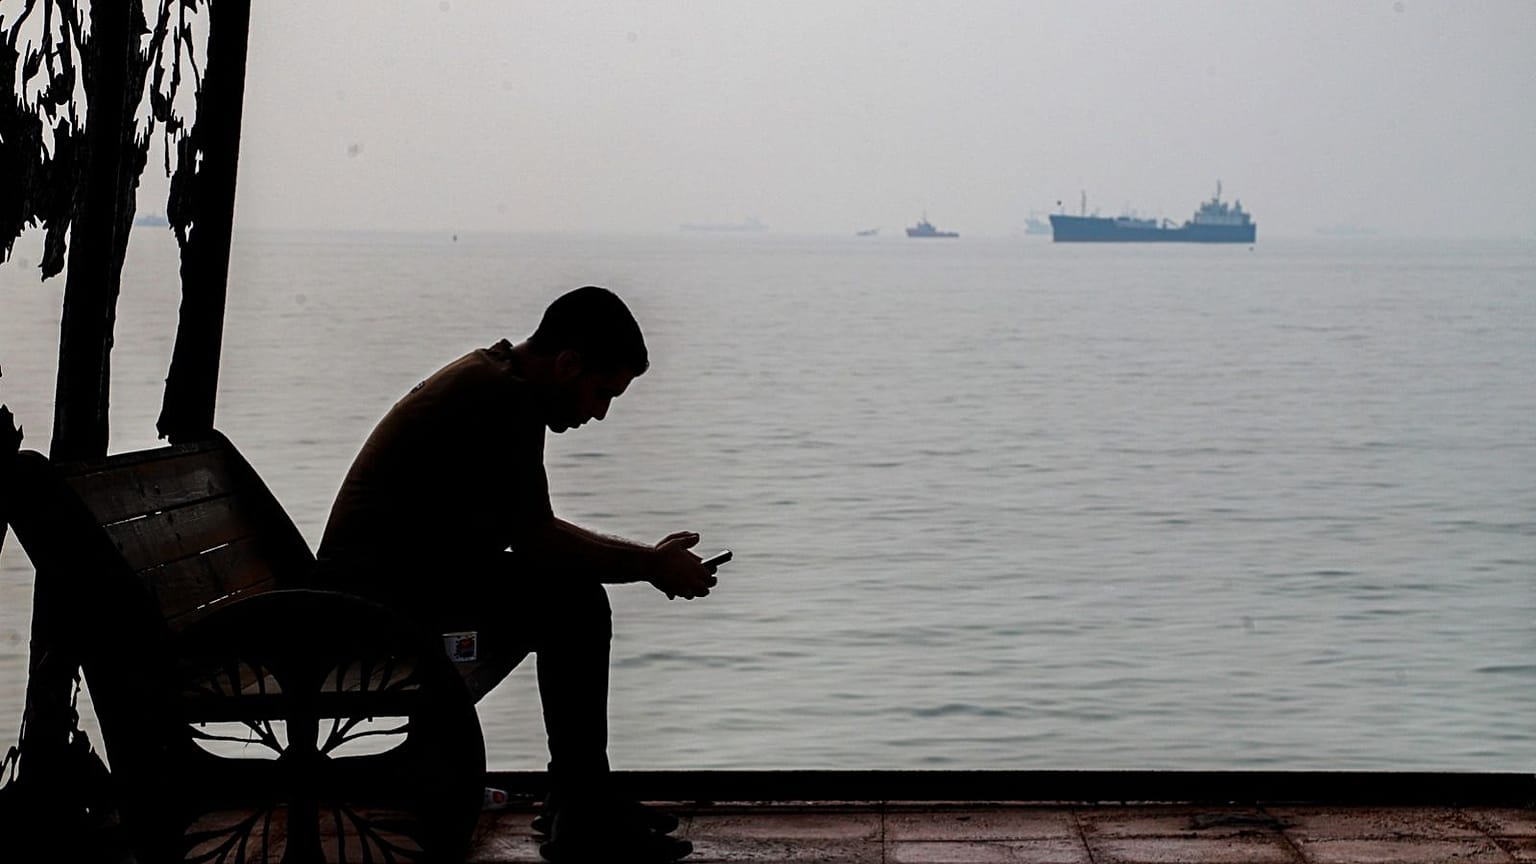
A man checks his cellphone at a waterfront shelter as commercial vessels appear anchored in the Strait of Hormuz off Bandar Abbas, Iran, Monday, Tuesday, Oct, 6, 2026. (Amirho
Copyright AP Photo

By Euronews Persian with Euronews Romania
Published on

Euronews spoke to a crew member of a cargo vessel anchored off Pakistan for weeks and an Iranian maritime manager about dangers in the vital waterway — where traffic has fallen 90% since the war began and at least 95 seafarers in commercial roles have died.

The Al Ruwais, a 314-metre liquefied natural gas carrier flying a Bahamian flag, has been sitting adrift off the coast of Pakistan for weeks.

Fearing for its safety, its 34-member crew does not want to test the waters and attempt to cross the Strait of Hormuz, despite demands from the ship's owners.

"What strikes me as strange is that this company is willing to risk the ship just to pass through the Strait of Hormuz," an electrician aboard the UAE-owned vessel told Euronews.

"If it were up to the company, we'd go through, but for that to happen, the entire crew would have to agree. And they don't. I am waiting to leave by boat for Pakistan, where I will board another vessel."

Under maritime regulations, the right to refuse transit into a designated warlike area is individual, meaning that one sailor objecting is enough to stop a vessel from moving into a danger zone.

On ships whose crews do agree to cross, companies have offered captains up to $100,000 (€89,000) per month plus $50,000 (€44,500) risk bonuses, while ordinary crew wages have risen four to six times.

"On other ships, they give as much as $10,000 (€8,900), but not everyone gets the same amount, and it depends a lot on the position and base salary," the sailor aboard Al Ruwais told Euronews.

"It's only fair that everyone gets the same amount, otherwise, it would mean that the captain's life is worth more than that of the deckhand."

No passage is safe, sailors say

A vital waterway for the world's energy trade, the Straight of Hormuz has been under two concurrent naval blockades since the outbreak of the Iran war following US-Israeli strikes in late February.

The southern corridor near Oman is patrolled by US forces, while the northern route passes through Iranian-controlled waters. The IRGC Navy has stated that vessels transiting routes it considers unauthorised face what it described as "punitive action".

Traffic through the strait has collapsed as a result. More than 125 vessels passed daily before the war. That figure has fallen to fewer than 10 to 12, a drop of more than 90%, according to ship-tracking firm Kpler.

Drone attacks, sea mines and strikes from unknown projectiles have driven the decline, with UK Maritime Trade Operations recording multiple incidents involving fires, sinkings and power failures aboard tankers and LNG carriers.

Ships that do attempt the crossing have taken to turning off satellite AIS transponders, extinguishing running lights at night and shutting down radio equipment to avoid detection.

IRGC boats navigating the Strait of Hormuz
IRGC boats navigating the Strait of Hormuz AP Photo

The dangers are somewhat different for Iranian sailors. Hamed, a 50-year-old former captain who now runs a maritime management company in Iran, told Euronews that since March of last year the war has resulted in the deaths of some 95 seafarers in commercial, fishing, passenger, tugboat and offshore platform support roles.

Military vessels have suffered heavy damage and ships undergoing repairs in Bandar Abbas have been struck, he said, although precise casualty figures have not been officially released.

"Nearly 60% of our ships are sanctioned and forbidden from calling at foreign ports such as India, Pakistan, the UAE, Oman, Kuwait, and Iraq," Hamed said. "Even Pakistan's maritime borders, where Iranian vessels used to travel, have now been closed to us."

Around 40% of southern Iranian seafarers have refused sea assignments, he said, with many shifting to the Caspian Sea to handle increased grain imports from the north. Wages in the south have been raised by 30 to 100%.

Sailors now earn between 50 and 80 million tomans (€165 to €265) per month, and captains between $1,200 and $4,000 (€1,100 to €3,700).

US forces have boarded Iranian commercial vessels roughly 15 times since the war began, Hamed said, arriving by helicopter and speedboat to inspect cargo for explosives, with no guarantees of their safety.

“The US has provided no safe-passage guarantees for Iranian commercial ships," Hamed said. "Every week we witness aerial or naval drone attacks on Iranian vessels."

He estimated that roughly 35,000 Iranian seafarers across approximately 2,000 vessels continue operating in southern waters to deliver wheat, corn and medicine to ordinary Iranians.

If the situation deteriorates further, he warned, authorities could be forced to declare a complete shutdown and evacuate coastal facilities.


Iran's IRGC says it hit four ships in the Gulf as three more strike mines

Iran's IRGC says it hit four ships in the Gulf as three more strike mines
Image released by IRGC of alleged strike. / CC: Iranian media.Facebook
By bne IntelliNews October 22, 2026

Iran's Islamic Revolutionary Guard Corps (IRGC) navy said it struck four vessels transferring oil ship to ship in the northern Persian Gulf, Hamshahri Online reported on October 22.

The IRGC said all four vessels were hit at the same moment and are burning.

It did not name the ships, their flags or their owners, and gave no casualty figures. The claim cannot be verified.

The statement presents the Strait of Hormuz as a waterway the IRGC navy manages and controls. It says the four vessels had earlier used illegal routes despite warnings to shipping companies.

Three more vessels caught fire and stopped overnight after hitting mines west of the strait, it said. It blames Washington for steering ships into a mined passage, which it says causes more accidents by the day.

The IRGC warned that if the US persists, confrontation will extend to what it called aggressor bases in the region. It described the message as a serious warning.

The US and Iran have been at war since late February, and Iran effectively closed Hormuz when the fighting began.

Donald Trump announced on July 13 that the US would reinstate a blockade on Iranian shipping, barring Iranian vessels and ships serving Iranian customers from the strait, and said it would levy 20% on cargo.

US Central Command says forces have diverted 70 commercial ships, disabled three and boarded two since the blockade resumed on July 14.

The IRGC runs its own permit system, charging up to $2mn a tanker for a corridor near Larak Island, and Chinese-flagged ships have kept using it.

Iran's foreign ministry has defended its Hormuz blockade and tanker strikes as lawful self-defence. Three Iranian tankers have left the blockade in the first crude exports in two months.

US Treasury Secretary Scott Bessent has called the blockade and the widening sanctions a "one-two punch" meant to force Tehran to reopen the strait.