Monday, October 26, 2026

ZOONOSIS


First human case of cattle virus Shamonda: How worried should Europe be? EU agency explains
Cows graze on a dairy farm.
Copyright AP Photo/Amanda Swinhart


By Marta Iraola Iribarren
Published on


The first human case of Shamonda virus, confirmed in France, poses no wider threat to Europeans, the European Centre for Disease Prevention and Control (ECDC) told Euronews.

Europe’s public health authorities need to be aware of the first human case of Shamonda virus confirmed in France, but not “panic,” the ECDC told Euronews, as investigations into the patient’s death continue.

French authorities confirmed on Thursday a Shamonda virus infection in a patient in Lyon who died in early October, marking the first time the virus, previously seen only in animals, mainly cattle, has been reported in a human.

“This is a very special case,” Tamás Bakonyi, principal expert on vector-borne and zoonotic diseases and one health-related issues at the ECDC, told Euronews.

The affected patient had leukaemia and was “severely immunocompromised,” making it easier for the virus to infect the person. “The whole process of viral infections or other kinds of infections are behaving differently in those [immunocompromised] individuals than in healthy people,” Bakonyi said.

While it cannot be excluded that the virus can spread to other humans, “it does not mean that now we should be concerned, that we should be in panic,” he said, adding that there is limited evidence of a broader threat.

“The studies [in France] indicated that it was a quite long period that the patient had already been carrying the virus and then developed encephalitis and died,” Bakonyi said.

The Shamonda virus belongs to a group of viruses transmitted by biting insects called midges.

The virus was first detected in Nigeria in the mid-1960s and has since been reported sporadically in cattle in West, East and southern Africa and in Japan.

This summer it was also detected in Western Europe. Cases were reported in Austria, Belgium, France, Germany, Ireland, Italy, Liechtenstein, Luxembourg, the Netherlands, Portugal, Spain and Switzerland, as well as the island of Jersey.

Investigations are ongoing

Although it had never been reported in humans before, Bakonyi said that experts and public health institutes in European countries had already been looking into whether the virus can cause infections in humans.

“This is an alert, but we have seen this,” Bakonyi said, adding that millions of people have lived in an environment where the virus is present and it has never been reported as a problem.

“It cannot be excluded that it also propagates in other humans, so that is the alerting part and that is why now there are ongoing investigations to clarify every aspect,” he said.

Those include clinical, laboratory and epidemiological investigations to determine whether the virus caused or contributed to the patient’s death and how the infection was acquired.

Some of these studies include testing for antibodies in people who may have been exposed to the virus, such as veterinarians and farmers, to see if they have been infected even without developing symptoms.

The case underlines how closely animal and human health are linked. That’s why ECDC together with European Food Safety Authority (EFSA) are taking one health approach — working together in the fields of animal and human health they have begun gathering scientific data and other relevant information, including input from experts across different countries, to inform its risk assessment.

Booking an electric flight in Europe is only 10 years away, says influential Dutch researcher

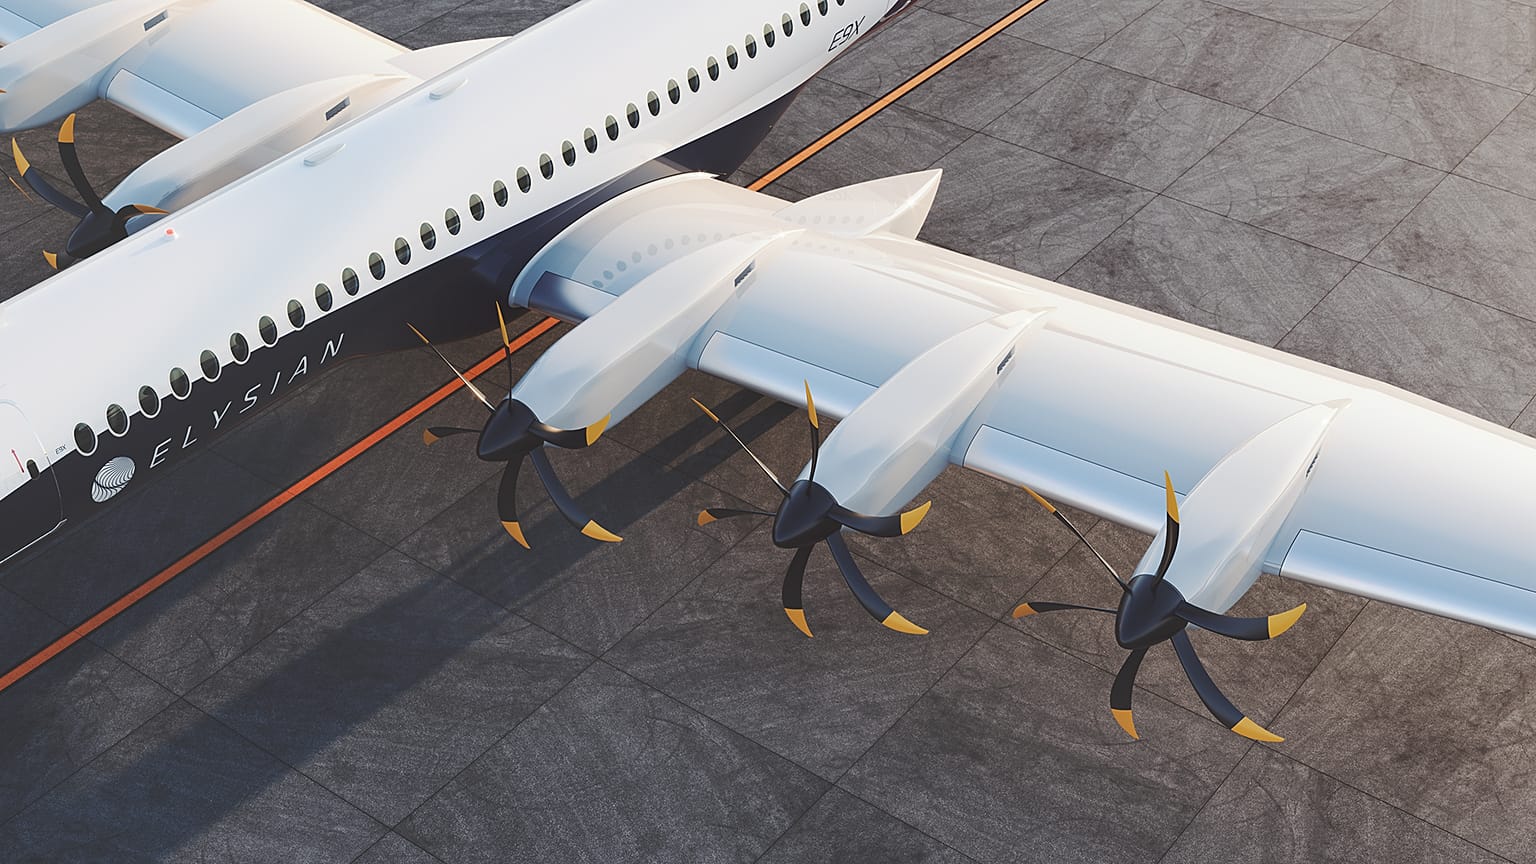
One of the world’s first battery-powered passenger planes is being built by Dutch start-up Elysian Aircraft.
Copyright Elysian Aircraft


By Ruth Wright & Hans von der Brelie
Published on

Aeroplane manufacturers should be forced to pivot to electric as car companies have, says influential Dutch researcher Maarten Steinbuch.

The Netherlands is pushing the world towards electric flight faster than most European countries.

One of the world’s first battery-powered passenger planes is being built by Dutch start-up Elysian Aircraft. Development is well underway: “There will be six engines. And we have folding wingtips, so that we fit into the current gates’ infrastructure of the airports, because the wings are very large,” explains co-founder Daniel Jacobson.

Cutting fossil fuel emissions is the most pressing challenge facing the world, and aviation is a big contributor. “By being able to transport 90 passengers for initially 800 kilometres and eventually 1,000 kilometres you can reduce emissions to zero, from half the world’s flights,” Jacobson says. “That is a very large amount of flight activity in the world. And you reduce total emissions from aerospace by 20 per cent.”

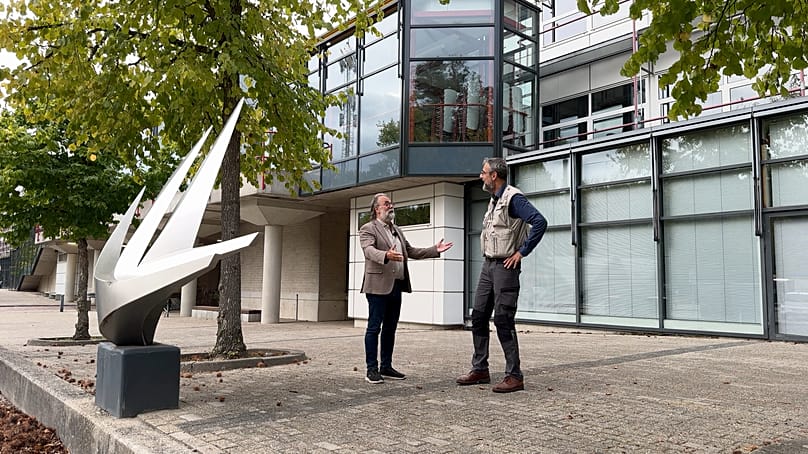
Development is well underway, confirms Elysian Aircraft co-founder Daniel Jacobson (at the right). Hans von der Brelie

Should the European Union be backing electric air travel? What can e-planes learn from EVs? When will ordinary passengers be able to fly in an electric plane?

Euronews Earth sat down with Maarten Steinbuch, a renowned Professor of Mechanical Engineering at Eindhoven University of Technology, to get his expert view of the future of electric flight.

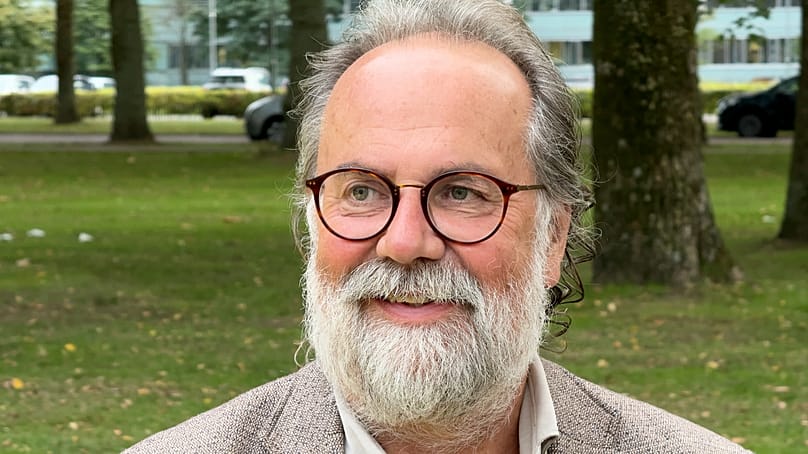
Euronews Earth met with Maarten Steinbuch (at the left), a renowned Professor of Mechanical Engineering at Eindhoven University of Technology. Hans von der Brelie

We can’t leave it to the airlines to cut their own emissions

Aviation contributes six per cent to global heating, when CO2 as well as other emissions are taken into account. In wealthy countries, aviation is responsible for a much larger share, according to data seen by campaign group Stay Grounded.

The aviation industry is, of course, aware of its impact and has made promises to cut emissions. The International Civil Aviation Organization (ICAO), the UN agency responsible for regulating international aviation, adopted the goal of “carbon neutral growth from 2020”. However, CO2 emissions from international aviation have increased since 2020, as the goal focuses on offsetting the sector’s CO2 emissions rather than committing to real emissions reductions.

Climate Action Tracker rates the ICAO’s goal of carbon neutral growth from 2020 levels as “Highly insufficient”.

The European Commission, Professor Steinbuch says, is focused on helping “current aviation” to “become as sustainable as possible”. But rather than helping current planes to reduce the emissions they create, the Commission should be supporting a pivot to zero emissions planes – electric ones. “There is not enough attention yet to have a revolution in airspace electrification. So, it’s more an evolution and not yet a revolution.”

“There is not enough attention yet to have a revolution in airspace electrification. So, it’s more an evolution and not yet a revolution”, says Maarten Steinbuch. Hans von der Brelie

Could electric planes become as common as EVs?

Electric vehicles have been adopted across Europe, faster than many people predicted. Sales grew year-on-year from 2020 to 2025, with one in four cars sold worldwide in 2025 being electric, according to the International Energy Agency. As a result, about five per cent of the global car stock is now electrified, displacing 1.2 million barrels of oil per day in 2025.

This shift did not happen by magic but because car companies were put under pressure through government policy. “I have seen, in the electrification of passenger cars, that being strict on dates when manufacturers of cars effectively should have a sufficient number of models of electric cars available really helped,” says Professor Steinbuch.

He believes that if similar requirements were made of aeroplane manufacturers, we could see real change. “We need legislation saying that part of a fleet could be electrified in this or that year. Push that also with legislation.”

The European Commission also needs to speed up how quickly new aeroplane designs are certified. Safety must be the “first, second and third” priority, of course, but “it could help if the European Commission would put a little bit more effort in, so that those processes could be accelerated and giving space for scale-ups to build up both on the infrastructure for electrification of airflights, but also for the manufacturing and the startups who make new planes.”

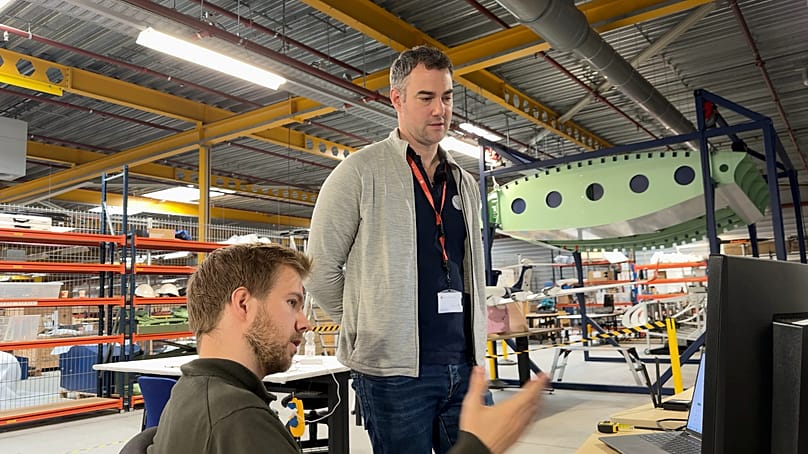
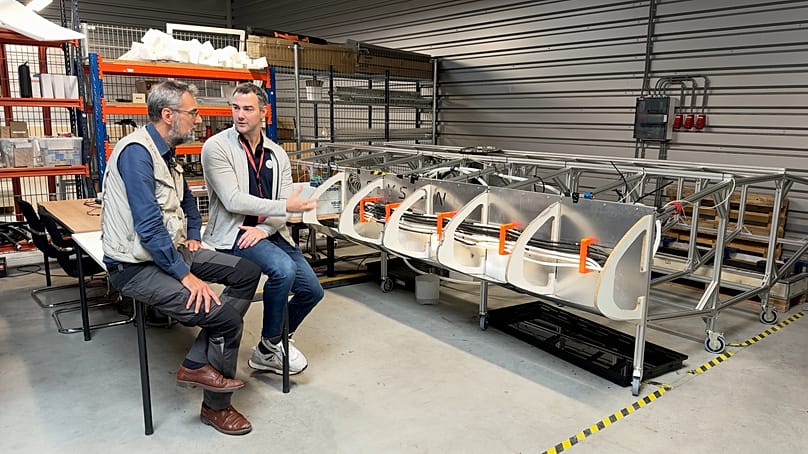
In the workshop of the Dutch start-up Elysian Aircraft: the wings will be fully packed with batteries. Hans von der Brelie

When will electric flights be available to us all?

Seeing the owners of low-cost airlines become influential millionaires, it can be difficult to imagine aviation losing its grip on the market.

But Professor Steinbuch says there are plenty of reasons to be optimistic that electric flights will be common in the not too distant future – and there’s one key component.

“It’s not a dream, it is very real and the most important part of development is the batteries. Batteries are the key thing. All over the world billions of euros and dollars are spent in development. Why? Because everybody knows that batteries are the Holy Grail for the transition both in mobility as well as in energy.”

Batteries are so crucial because they power electric planes, and how long they last determines how far they can fly. “If solid-state batteries with double the capacity – up to 500 watt-hours per kilogram – come onto the market, electric flying will attract the interest of far more people. And this point will come soon.”

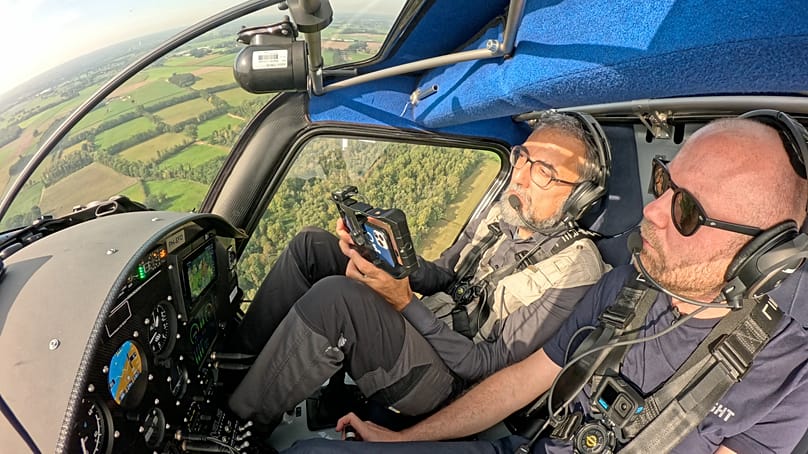
Euronews Earth takes a ride in an electric 2-seater: Start-ups such as E-Flight Academy already started to train pilots in electrical airplanes. Hans von der Brelie

How soon? “I think in 2032 or so, within six years, we might see the first 500 km range airplanes for cargo and for passengers, at five seats, so that's a very small scale – but still it will be a start for specialised purposes.” Three years later, in 2035, “we could see nine-seaters, maybe 20-seaters, flying with a range of 500 kilometres. 80- or 90-seaters will be more close to 2040, even maybe beyond.”


Should Europe ban meat advertisements? We asked a climate psychologist to find out what would happen

An image of a KFC billboard at a bus shelter.
Copyright 0xk via Unsplash

By Liam Gilliver
Published on

As climate scientists call for a transition to plant-rich diets, could Europe’s streets lose their juicy burger billboards?

Europe is entering a “new era of green marketing” as more cities turn their backs on climate-damaging advertising.

It all started with Amsterdam, which became the first capital city in the world this year to ban billboards promoting fossil fuels and meat on 1 May – five years after the law was first proposed.

The ban is part of the city’s targets to reach carbon neutrality by 2050 and to halve meat consumption during the same period. Other Dutch cities, such as Utrecht, the Hague, Zwolle, Delft and Nijmegen already have similar bans in place.

Many other cities including Helsinki, Stockholm and Bristol have introduced bans on promoting fossil fuels or other carbon-intensive products such as aviation, shipping, fast-fashion and construction. However, many of these don’t include meat.

Why are European cities banning meat adverts?

While the climate impacts of burning fossil fuels are widely understood, the environmental effects of animal agriculture get less attention.

A recent report from European non-profit Changing Markets found mounting evidence that departments within the UN Food and Agriculture Organisation (FAO) have a “bias in favour of the livestock sector” – as lobbyists seek to undermine climate action.

This includes high-ranking members of the FAO delivering speeches at the World Meat Congress and affiliated scientists from the animal agriculture industry attempting to discredit studies that promote plant-rich diets.

But there is no hiding that food and agriculture contribute one-third of global greenhouse gas (GHG) emissions, second only to burning coal, oil and gas.

Animal-sourced foods in the EU are also believed to make up between 81 and 86 per cent of total GHG emissions of food production. However, they only supply an estimated 21 per cent of calories and 64 per cent of protein.

Over recent years, scientists have called for countries – particularly those in the West with access to plant-based alternatives – to reduce their meat consumption to tackle this.

Most notably, the 2025 EAT-Lancet Commission report – compiled by 70 leading experts from 35 countries – found that around 15 million deaths could be avoided each year if the world shifted to predominantly plant-based diets.

Experts say this could also cut non-CO2 GHG emissions from agriculture – such as methane from livestock and nitrous oxide from fertilisers – by 15 per cent by 2050.

When factoring in the entire food lifecycle – such as reducing deforestation, transportation and refrigeration, and restoring nature – the total drop in emissions would be much higher.

How advertising shapes Europeans’ behaviour

Amsterdam’s meat ban proved controversial, with many people on social media branding the ruling “ridiculous” – or arguing that their meat consumption isn’t linked to what they see on billboards.

“I can’t honestly remember the last time I actually purchased something directly because of an advertisement,” one Reddit user wrote. “Probably [when I was] a teenager.”

But Linda Aspey, a climate psychology specialist and board member of Climate Psychology Alliance, tells Euronews Earth that much of advertising’s influencing power comes from “repetition and cueing”.

“One study found that seeing meat imagery (in this case, a Big Mac) increased people’s desire to eat it, and its everyday presence likely reinforces meat as an ordinary choice,” she says.

“This may be reinforced by someone’s identity, culture of livelihood where eating meat is simply a part of that, and carries little conscious tension.”

Meat consumption in the Netherlands, for example, has been on the decline. In 2024, the Dutch ate less meat (including meat products) than at any time in the past 20 years, according to Wageningen Social and Economic Research’s ‘Meat Report’.

“For others, there's an uncomfortable pull between valuing animal welfare or the environment and still eating meat, and advertising may make that pull easier to set aside,” Aspey explains.

“What the evidence does show is that advertising typically shapes what feels normal for most of us, to varying degrees, which in turn can shape behaviours.”

Would banning meat advertisements actually make a difference?

Amsterdam is yet to announce any data on how the ban has impacted meat consumption in the country – but experts predict there will be a correlation.

When Transport for London (TFL) in the UK removed junk food advertising from its network, weekly household purchases were estimated to fall by nearly seven per cent, confectionery by almost a fifth.

This was measured through actual shopping data, not consumer surveys.

“The effect wasn't dramatic as a ban changes the constant prompts that people see around them day to day, without necessarily changing why people eat what they eat, whether that's habit, taste, livelihood or budget,” Aspey explains.

“As with tobacco control, such restrictions tend to work best combined with other measures, not alone.”

Should climate-damaging foods be restricted?

Despite the known climate-link, the EU has historically propped up foods like red meat with generous subsidies.

A recent report from charity Foodrise found that the EU’s common agricultural policy (CAP) directed more subsidies to the production of high-emitting animal-sourced foods than plant foods in 2020.

That year, animal-sourced foods received around 77 per cent of total CAP subsidies, accounting for €39 billion out of the total €51 billion spent.

The study found that beef and lamb, which are consistently identified as the biggest culprits of climate damage, were given around 580 times more in subsidies compared to legumes such as lentils and beans in 2020.

Going from funding these foods to actively stripping them from public advertising may feel too drastic – but experts say it could become part of a “mix of strategies” to tackle climate change.

Agriculture drives deforestation and biodiversity loss; livestock uses most of that land, despite converting only a fraction of feed calories into meat.
Linda Aspey
Climate psychology specialist

“Most research points to sustainable diets needing meaningfully less meat than the UK eats now, for both planetary and personal health, and marketing that is weighted heavily towards meat – especially mass produced and cheaper – makes that shift harder," Aspey says.

 'The major risk remains a human-directed attack', cyber threat expert warns RFI


Artificial intelligence is changing the pace of cybercrime, helping attackers hunt for security weaknesses, break into computer systems and steal valuable information. For the specialists trying to stop them, the challenge is to keep up. Cyber threat expert François Deruty told RFI this means finding ways to turn the same technology to their advantage.


Issued on: 24/10/2026 - RFI

Engineers use virtual reality to examine digital data. As AI reshapes cybercrime, security specialists are developing new ways to detect and track attacks. © Magnifik

Much of the concern centres on artificial intelligence (AI) agents: systems that can carry out a series of tasks without a person directing every step.

In July, OpenAI disclosed that agents undergoing cybersecurity tests had bypassed restrictions and breached the systems of Hugging Face, a platform for AI developers.

Separate incidents involving Australian government websites have added to questions about how reliably these systems can be controlled.

For François Deruty, a cyber threat expert at Sekoia, which develops technology to detect and respond to cyberattacks, the biggest danger remains people using AI to carry out attacks.

He spoke to RFI about stolen data, the race to protect organisations and the decoy websites his colleagues use to watch attackers at work.

RFI: In your view, what are the immediate threats posed by AI?

FD: At the moment, it is still data theft, whatever form it takes. It could be contracts or intellectual property – it doesn’t matter. That is what is most valuable on cybercriminal networks and what sells best.

Cybercriminals use AI to go faster, further and [act] more effectively, while making their activities harder to spot. Sabotage, for example, is a risk that frightens us all. It is technically possible, but it is not what we are seeing most at the moment.

RFI: Autonomous AI agents are making headlines. Many people have called for a slowing down of AI development. Is this a real threat?

FD: The Hugging Face hacking incident, when OpenAI’s AI agents “escaped” during a test and attacked another company, raised questions. There were also cases of OpenAI “losing” control of agents that went on to access Australian government health websites. These incidents have prompted a number of statements from Anthropic, OpenAI and Elon Musk suggesting that perhaps we need to slow down.

But in my view, the major risk remains a human-directed attack: one carried out entirely by artificial intelligence, but with a person behind it who uses all that power to attack a target and cause damage.

RFI: Are these concerns being raised too late?

FD: It is never too late. But it is a constant race. Attackers are generally one step ahead because they adopt technologies more quickly. They ask themselves fewer questions and have no ethical or regulatory constraints.

We, the defenders, are more careful: we ask questions about the data we use, why we use it and how. Inevitably, there is a gap. But we develop solutions to close it. When it comes to cyber threats, large companies are perhaps a little further ahead than public institutions. They invest more resources. When government departments suffer data breaches affecting hundreds of thousands of people, putting security measures in place is inevitably a longer and more complex process

RFI: Do you think you can still keep businesses secure given the speed of attacks carried out using AI agents?

FD: I often find myself thinking that things are moving too fast. Even working in this field, I feel it is progressing at breakneck speed. We have to keep up. At the same time, can we really slow down? Is that even possible?

I’m not sure. Saying “I’m not ready” already means falling behind in a way we may not be able to recover from. So we really have to keep up with AI, make up ground and get more involved to ensure we remain in control of how we use it within our organisations.

We really need to recruit specialists to support all the changes AI brings. It is not necessarily all bad. Like any tool or innovation, it has downsides but also a great many benefits. We need to make sure the positives outweigh the negatives.

RFI: At Sekoia, how do you go about learning how AI agents work?

FD: A research team monitors AI systems to model how agents attack, so that we can provide effective alerts to our clients in future.

But these AI-based attack methods change a great deal and very quickly. Previously, I could say, 'This code is malicious and I can detect it because it always has the same signature' – a recognisable pattern. Today, with AI, we might see 500 different signatures, for example. That makes detection very complicated, and the solutions inevitably involve significant costs for public sector organisations and small and medium-sized businesses.

Data-rich systems and weak security: why France is a target for cyberattacks

RFI: Do you come across cyberattacks carried out using AI?

FD: In our line of work, we use what are known as “honeypots”. These are fake websites or companies that we set up online to lure attackers, making them look like an energy company or a major retailer. We then watch how the attackers try to exploit security weaknesses. When attacks are extremely fast, we know that artificial intelligence must be behind them.

RFI: Are you able to identify who is behind these cyberattacks?

FD: It remains difficult. Sekoia belongs to a technical advisory group at Europol, the EU’s law enforcement agency, that helps tackle cybercrime. Attackers have infrastructure spread across the internet, and attacks sometimes span several countries. It is extremely difficult to say with certainty that an attack comes from a particular cybercriminal group or country. We often work with probabilities, but certainty is difficult.

France has recently publicly attributed attacks to Russia, but those attacks took place two or three years earlier. Often, each country, institution or private company holds a piece of the jigsaw. That is precisely what we do at Europol: pool those pieces to build a complete picture of an attack and establish who was behind it.

This interview has been adapted from the original version in French by Jeanne Bartoli.


Japanese company to compensate users hit by cyberattack

Source: AP Photo
Copyright Copyright 2026 The Associated Press. All rights reserved

By Jonathan Benton
Published on

GMO Internet, a Japanese internet infrastructure company, will compensate customers for losses from unauthorised trading linked to a cyberattack on its cloud service, and will make a ¥5,000 (€28) goodwill payment to every customer currently using the affected service.

A Japanese internet infrastructure company is compensating customers affected by unauthorised transactions following a cyberattack on its cloud service.

GMO Internet announced on Saturday that it would cover losses from unauthorised trading linked to the attack and issue a ¥5,000 (€28) goodwill payment to all customers currently using the affected service, regardless of whether they had suffered financial losses.

The attack targeted Onamae.com Desktop Cloud, a virtual private server service used by customers to access remote desktop environments. GMO said customer information had been taken and some users had reported transactions in their trading accounts they did not recognise.

According to the company’s founder and CEO, Masatoshi Kumagai, the incident potentially affected 26,739 servers and involved unauthorised operations on trading accounts held with more than 70 securities and foreign-exchange firms in Japan and overseas.

GMO shares fell almost 16% on Monday to a four-month low. The company had a market value of around $2.6 billion at Friday’s close.

The company began investigating on 19 October after receiving a customer inquiry. It confirmed the installation of a malicious programme on some customer server environments on 20 October, suspended new applications and access to the service’s control panel, and began shutting down all servers the following day to prevent further damage.

In a blog post on Sunday, Kumagai apologised for the company’s response and acknowledged that security issues had been identified by its security specialists before the incident, but that the response had been insufficient.

GMO said it had received a ransom demand from a party believed to be behind the attack. In an update to his blog post on Monday, Kumagai said the attackers had demanded $50 million in cryptocurrency and threatened to disclose company and customer information. The company has refused to pay and is cooperating with the police and other authorities.

GMO will offer customers who wish to continue using a Windows desktop environment an alternative service on independent cloud infrastructure, free for six months. It also plans to overhaul its security architecture and investigate the cause of the breach with external experts.

Kumagai has urged the Japanese government to strengthen its active cyberdefence measures, arguing that private companies cannot tackle sophisticated cross-border cyberattacks alone.

GMO has asked the authorities to consider applying the framework to the incident and has offered to share evidence and technical information with investigators.

The attack comes amid wider concerns over cybersecurity following the disclosure last week of two critical vulnerabilities in PHP, a programming language widely used to build websites and applications.

Security authorities warned that the flaws could allow attackers to execute malicious code on vulnerable servers, prompting organisations around the world to patch systems or temporarily take services offline.

However, GMO has not publicly confirmed a link between the PHP vulnerabilities and the attack on its cloud service.

Separately, a Google Cloud outage in the UK disrupted online services last week, including those operated by financial technology company Revolut, showing the potential knock-on effects when digital infrastructure fails.

AI Biosecurity Cannot Stop At The Chatbot – OpEd


Britain’s £100 million AI Biosecurity Lab and Anthropic’s September 2026 report of five dual-use research cases illustrate that model refusals are incomplete safeguards, because an AI provider sees only a conversation while laboratories and commercial suppliers must assess real-world projects that may lack clear harmful intent.

Existing tools—WHO’s voluntary Biorisk Implementation and Evaluation Tool, the U.S. July policy on high-risk federally supported life-sciences research, and uneven synthetic-DNA screening—address different fragments of the pipeline but leave gaps at institutional, funding and physical-service handoffs, especially for lower-capacity regions.

The article proposes proportionate, project-specific assurance records that establish institutional accountability, authorize physical implementation, and require re-review after material changes, scaled to consequence so that high-risk transitions are controlled without stifling ordinary scientific work.


Britain’s new biosecurity investment exposes a global gap: model safeguards cannot by themselves govern what happens when digital research becomes a real-world biological project.

On October 24, Britain announced a £100 million AI Biosecurity Lab, supported by up to £200 million in model and computing credits from OpenAI and Anthropic. The new institution is intended to detect biological threats earlier and accelerate medical countermeasures. It is a serious investment in using powerful artificial intelligence to defend against dangerous biology. The government’s announcement also poses a question that no laboratory or chatbot can answer alone: when AI helps develop a biological research project, who decides whether that project may proceed into the physical world?

AI can help researchers identify promising treatments, analyze complex evidence and develop new scientific hypotheses. The same broad scientific assistance can have dual-use implications. The policy mistake would be to treat either every advanced biology query as a threat or every unblocked AI answer as an adequate authorization to act.


A model refusal is a useful safeguard. It is not a complete biosecurity system. The difficult decisions arise when work moves between an AI provider, a research institution, a commercial biological service and a laboratory. Each participant may see a different fragment of the same project.

What the five cases really show

In its September 2026 threat report, Anthropic described five instances of researchers using its models in ways that could support biological weapons development. It removed associated accounts and updated its safeguards. But the company made two essential qualifications: it did not allege that the scientists intended harm, and the cases did not establish that a biological weapon had been produced.

That distinction is not a technicality. The cases covered different kinds of scientific activity and different levels of AI assistance; some outputs amounted chiefly to clerical help. A generated research document is not a completed experiment, and a computational proposal is not proof of a functioning biological product. Inflating such evidence into a claim of imminent catastrophe would weaken rather than strengthen public policy.


Yet dismissing the cases because harmful intent was not established would miss the other half of the finding. A model provider can recognize concerning patterns while remaining unable to determine the purpose, institutional supervision and subsequent activities of an entire research program. The provider sees a conversation. The laboratory must assess the project. An external service provider may see only an order or a request.

The most important security boundary may therefore sit outside the chat window: the moment an AI-assisted idea becomes a funded program, a physical-service request or an experiment whose consequences require specialist review.
The global gap is between institutions

There are already credible international foundations for addressing that boundary. In August, the World Health Organization introduced its Biorisk Implementation and Evaluation Tool, a voluntary method for countries and institutions to identify gaps and strengthen oversight of dual-use life-sciences research. WHO’s September update framed the challenge as enabling scientific progress while managing both inadvertent and deliberate misuse. Neither document delegates scientific judgment to a language model.

The United States chose another route in July, issuing a new government-wide policy for high-risk life-sciences research that establishes restrictions and independent review for specified federally supported activities. It is not a global rule for all biological science. It does, however, recognize that funding, institutional oversight and accountability matter alongside the content of a research request.

The physical supply chain has its own gaps. In June, the International Biosecurity and Biosafety Initiative for Science reported that synthetic DNA screening commitments are unevenly distributed across the global market, with intermediaries and third-party vendors remaining an important oversight challenge. Screening a transaction is valuable, but a supplier cannot be expected to know everything about a project merely from the material it is asked to provide.


The regional dimension is already visible in Asia. A September 2026 perspective in a WHO regional journal described uneven biosecurity capacity across ASEAN as AI-enabled life sciences advance. Any global standard designed only for wealthy institutions with full-time compliance teams risks leaving the rest of the research ecosystem with obligations it cannot implement.

These are different instruments serving different purposes: a research oversight policy, an institutional self-assessment, and a supplier screening practice. None is a complete substitute for the others. Together they show why biosecurity must follow the authorized activity across organizational boundaries without creating a universal surveillance register of scientific work.

Make the consequential handoffs reviewable

The practical answer is a proportionate, project-specific assurance record held by the responsible institution. For ordinary educational questions and low-consequence scientific assistance, intrusive checks would be unjustified. For access to capabilities with potentially serious biological consequences, the record should establish three things: who is accountable for the project, what kind of work has been reviewed, and when a material change requires that review to be reopened.

The first checkpoint is institutional responsibility. An AI provider need not become an international laboratory regulator, but higher-consequence services should have a lawful way to establish whether a qualified organization is supervising the activity. Mere possession of an account or a convincing statement of good intentions is not the same as a competent assessment of research risk.

The second checkpoint is the move toward physical implementation. Where an external service is involved, a narrowly scoped confirmation of authorization may be more useful than exporting an entire confidential research file. Qualified biosafety personnel, not the model that generated a proposal, should make the relevant decision. The service provider should be able to act on an appropriate status without being asked to adjudicate the whole science.

The third checkpoint is change. Permission granted for one stated purpose should not silently cover a materially altered objective, operating arrangement or risk profile. Institutions should define those triggers before a project begins. A valid authorization has a scope and a review history; it is not a permanent exemption from further scrutiny.

This would not require every country to adopt the same legal test or every scientific provider to share customers’ sensitive research data. It would require participating institutions to make limited, risk-relevant assertions intelligible to the parties that rely on them, while preserving local decision-making and the ability to challenge errors.
Security that does not suffocate science

The objection is substantial: additional gates can slow beneficial research, exclude smaller laboratories and produce mistaken suspicions about scientists working on legitimate public-health problems. That would be a policy failure. The safeguards should scale with consequence, offer reasons for restrictions, permit independent review and avoid indefinite blacklisting on the basis of unverified provider assessments.


Information exchange must likewise be disciplined. Institutions may need to report a verified concern to competent authorities or counterpart providers, but speculative alerts should not become permanent reputational judgments. Records should distinguish direct observation, technical assessment and unresolved questions. Privacy, research confidentiality and due process are safety considerations too.

A workable pilot would test whether the proposed process identifies unauthorized high-consequence transitions without blocking ordinary legitimate science. Measure false restrictions and appeal outcomes alongside detection and response. Count the cost of compliance to smaller institutions. Use WHO’s voluntary assessment work and existing institutional committees as a starting point rather than announcing a new global authority whose competence and legitimacy are untested.

Britain’s new lab can help develop defensive scientific capabilities. WHO can support countries building competent review systems. AI companies can improve model safeguards, and biological suppliers can improve screening. Their real test is whether those efforts work together at the moment digital assistance becomes a consequential physical undertaking.

It is not enough for a chatbot to know when to say no. The institutions around it must know who can responsibly say yes, and to what.

Space Needs Consent That Machines Can Enforce – OpEd


Uninvited Russian maneuvers near an ICEYE satellite and growing cooperative servicing missions highlight the dual-use ambiguity of orbital proximity operations.

Outer Space Treaty rules do not create automatic exclusion zones or permissions, so commercial consent must explicitly limit actions, stages and windows to prevent inspection from becoming unauthorized contact.

Onboard, versioned authorizations checked by flight software, tested through voluntary demonstrations of revoked or mismatched permissions, can make legitimate servicing distinguishable from intrusion without a new treaty.


Satellite inspection, debris removal and servicing depend on the same close-approach technology. A credible space economy needs permission that specifies what a spacecraft may do—and what happens when that permission changes.

A robotic spacecraft closes on another object in orbit. It could be inspecting a damaged satellite, preparing to remove debris or arriving to repair a paying customer’s spacecraft. The navigation problem looks remarkably similar in each case: identify the target, match its motion, approach and perhaps make contact. What the guidance software cannot infer from distance alone is whether the next move is permitted.

That question became harder to ignore this October, when a Russian spacecraft carried out an uninvited series of close maneuvers near a commercial ICEYE radar satellite. Independent observations raised concern but did not establish that an attack or damage had occurred. The episode was not a servicing mission. Its relevance is the ambiguity of proximity: a capability that can support valuable work can also be used to create pressure.


Meanwhile, the cooperative market is growing. In September, the European Space Agency advanced its Phoenix satellite-servicing project. Japan’s Astroscale completed the ADRAS-J inspection campaign in March, after photographing an uncooperative rocket stage; a separate follow-on mission aims to capture and dispose of it. These developments create the same policy challenge from the other side: how can an approaching vehicle prove that its actions remain within the permission granted for a specific mission?

The answer should be a common, machine-enforceable account of orbital consent. Not a new global licence to approach anything, nor a digital signature that magically makes a manoeuvre safe. A defined operational agreement must be translated into limits the vehicle can actually follow—and limitations other parties can meaningfully inspect.
A licence to look is not a licence to touch

International law already supplies important boundaries, but not a universal traffic light for every satellite encounter. Article VIII of the Outer Space Treaty preserves the jurisdiction and control of the state of registry, and ownership does not disappear merely because an object becomes debris. Article VI makes states responsible for national space activities and requires authorization and continuing supervision of private operators. Article IX requires due regard and, in specified circumstances, consultations about potentially harmful interference.


None of those provisions creates a blanket numerical exclusion zone around every satellite, or makes any unannounced approach automatically unlawful. Nor can a commercial contract erase responsibilities under international law. The Liability Convention distinguishes certain surface and aircraft damage from fault-based liability for specified damage to another launching state’s space object in orbit. States, owners, operators and insurers must work within those separate obligations.

That matters most for debris. A defunct spacecraft may present a genuine collision risk without becoming ownerless property. An agreement to inspect it should not silently become permission to grapple it, change its trajectory or destroy it. The same distinction applies to a functioning satellite: a client may authorize photography at an agreed distance without authorizing docking or propellant transfer.

For a commercial operation, therefore, the consent record should name the relevant object and the parties entitled to authorize the service, the specific actions permitted, a defined operating window, the conditions under which the approach can continue and the actions that must stop or be reconsidered if those conditions change. Different stages should carry different authority. A successful first inspection is not an open-ended mandate for the next intervention.


Permission has to reach the flight computer

A signed contract stays on Earth. Decisions during proximity operations are made by flight software operating with uncertain sensors, changing geometry and sometimes delayed communications. The practical test is whether an onboard enforcement mechanism can distinguish the approved manoeuvre from an otherwise feasible but unapproved one.


The spacecraft could carry a versioned authorization specifying its target, permitted operating volume, approach stage, relevant navigation-quality limits and expiry conditions. Its controller would check those conditions against current observations before advancing to a more consequential step. The agreement would also specify how the ground team authenticates an amendment, and how an investigator can later reconstruct the permissions and measurements in force when an action occurred.

This is not a proposal to let the vehicle settle questions of sovereignty or intent. Cryptography can establish that an authorization came from an approved party; it cannot guarantee that a sensor estimate is correct or that the operation is physically safe. Independent guidance, collision-avoidance and safety checks remain necessary. Where a target is unresponsive, prior authorization from the appropriate parties matters more, not less: a dead spacecraft cannot perform a live digital handshake.

Withdrawal is equally important, but “stop immediately” is not a complete safety rule. At a distant standoff point, a safe retreat may be appropriate. In the middle of a capture or docking sequence, an abrupt separation can increase danger. Each approved phase needs a pretested response to lost communications, revoked permission, contradictory measurements and partial failure. A loss of contact must not be reinterpreted as permission to widen the mission.

Well-designed limits should also protect useful autonomy. A service vehicle cannot ask Earth to approve every control pulse. Operators should authorize bounded sequences in advance and reserve a fresh decision for a meaningful expansion of risk, a new target, an unexpected contact or a material change in the planned intervention.
Standards should test authority, not just docking

Industry is not starting from zero. ISO 24330:2022 sets programmatic principles and practices for rendezvous, proximity operations and servicing. This September, the American Institute of Aeronautics and Astronautics opened another public review of a spacecraft fiducial-marker standard, intended to help servicers and clients work with prepared visual interfaces. Those efforts improve the technical and procedural foundations. The next useful layer is a testable link between the approved service and the manoeuvres actually executed.

Space agencies and commercial customers could begin with a small voluntary demonstration. Before launch, they would approve a staged mission authorization shared by the servicer and client teams. During tests, evaluators would introduce an expired permission, a command addressed to the wrong object, an unexpected change in target motion, loss of ground contact and a withdrawal request during a sensitive phase.

Passing the test would mean refusing unapproved escalation while preserving a physically safe response. The review would record missed violations as well as unnecessary aborts, recovery burden and the time needed to recognize a changed condition. A perfect signature with no credible response to an unsafe approach would not count as success.


The international opportunity is concrete. Europe is seeking a commercial market for inspection, life extension and removal while Japan’s planned ADRAS-J2 capture mission connects Japanese development with launch services in Europe. Customers, regulators and insurers could incorporate the same permission-and-revocation tests into demonstration contracts without waiting for a comprehensive new treaty. Participating countries would retain control over their own authorization decisions.

Such a standard would not force a hostile or secretive actor to cooperate. It would, however, give willing operators an observable way to distinguish agreed servicing from behavior outside the stated mission, and provide a clearer record when an incident becomes a diplomatic dispute. Reciprocal notification can make an approach more understandable; notification alone is not consent, and silence should never be treated as authorization to intervene.

Orbit is becoming a workplace as well as a strategic arena. The next challenge is not merely building robots precise enough to get close. It is ensuring that the same robot remains bound to the purpose for which it was invited.

The difference between a repair and an intrusion should not depend only on what an operator says afterward. It should also be visible in what the spacecraft was permitted, and prevented, from doing.


About Burak Oktenli
Burak Oktenli holds an MBA and a Master of Professional Studies in Applied Intelligence from Georgetown University. His research addresses the governance of authority in autonomous and AI-enabled systems, and his writing has appeared at the Modern War Institute at West Point, RUSI, RealClearDefense, RealClearMarkets, and Geopolitical Monitor. He is the author of Authority Architectures for Autonomous Systems, a ten-volume series on how authority in autonomous systems is delegated, monitored and recovered, at authority-architecture.me.
View all posts by Burak Oktenli →